Cyber Security for Healthcare
Referrals, records and research leave your organisation every day, and the digital estate carrying them grew faster than anyone documented. Hexiosec Transfer secures what you exchange. Hexiosec ASM maps what you expose, and produces the evidence DSPT asks for.
- UK Sovereign
- Cyber Essentials Plus
- DSIT Software Security Ambassador
- NCSC ACD 2.0 (ASM)
- Trusted by UK Government and regulated industry
Same patient data. Two directions of risk.
Transfer
The data you exchange
Referrals, records, research datasets and correspondence moving between trusts, practices, commissioners and suppliers, usually by email.
- Patient records and referrals
- Research and clinical trial data
- Correspondence with commissioners
- Supplier and contractor documentation
asm
The estate you expose
Trust and practice websites, patient portals, appointment systems and services built by departments over decades of reorganisation.
- Patient and staff portals
- Systems inherited through service mergers
- End-of-life software still serving the public
- Departmental sites nobody catalogued
Same patient data. Two directions of risk. Hexiosec covers both.
Two products, one sector. Start where your risk is.
Hexiosec Transfer: Secure the data you exchange
Encrypted exchange and secure forms for patient records, referrals, research data and supplier documentation.
Hexiosec ASM: See what attackers see
Continuous external discovery across a sprawling clinical digital estate, with DSPT evidence produced as you go.
Patient data should not travel by email
Clinical work depends on moving sensitive information quickly between organisations that all use different systems. Hexiosec Transfer gives you encrypted exchange and secure collection forms that work without asking the other side to adopt your tooling.
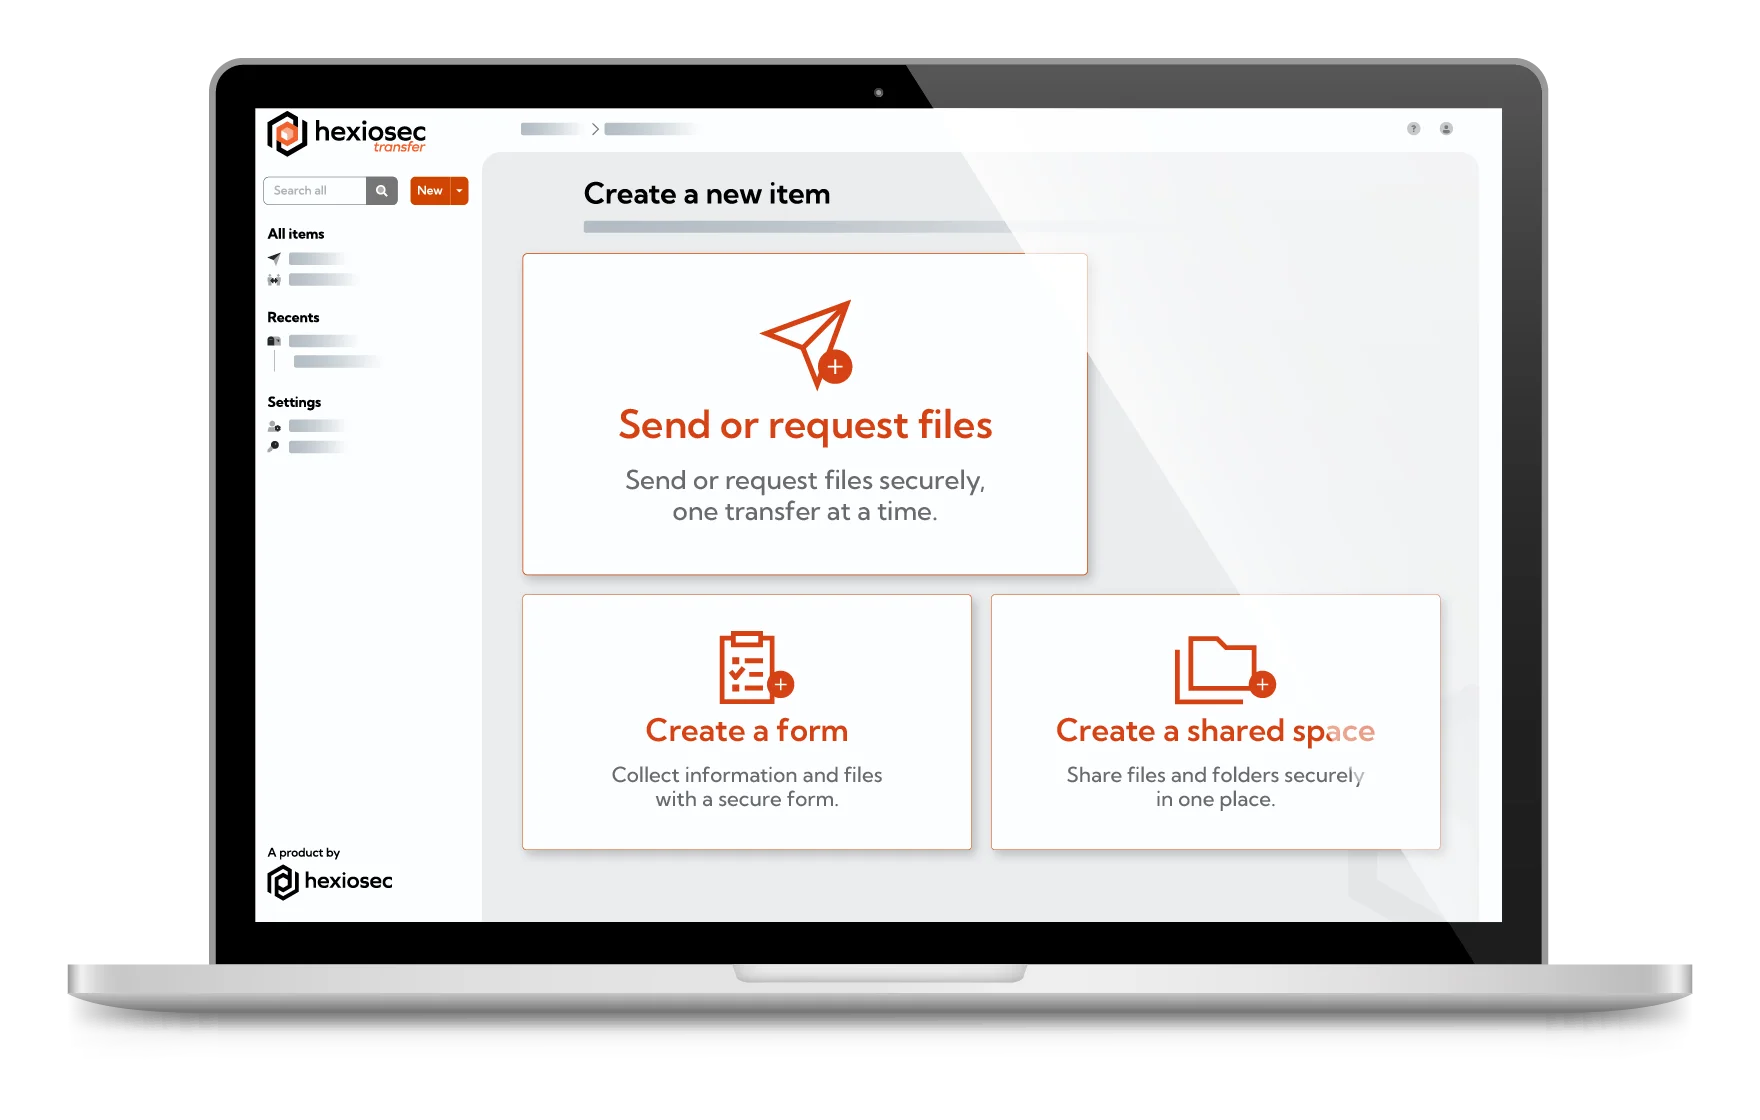
Records and referrals
Send patient information between organisations with end-to-end encryption and a full audit trail.
Research data
Share datasets with partner institutions and researchers under controlled access.
Secure collection forms
Gather documentation from suppliers, contractors and partners without email attachments.
UK sovereign throughout
Patient information stays in the United Kingdom, on infrastructure we operate.
A clinical estate nobody has fully mapped
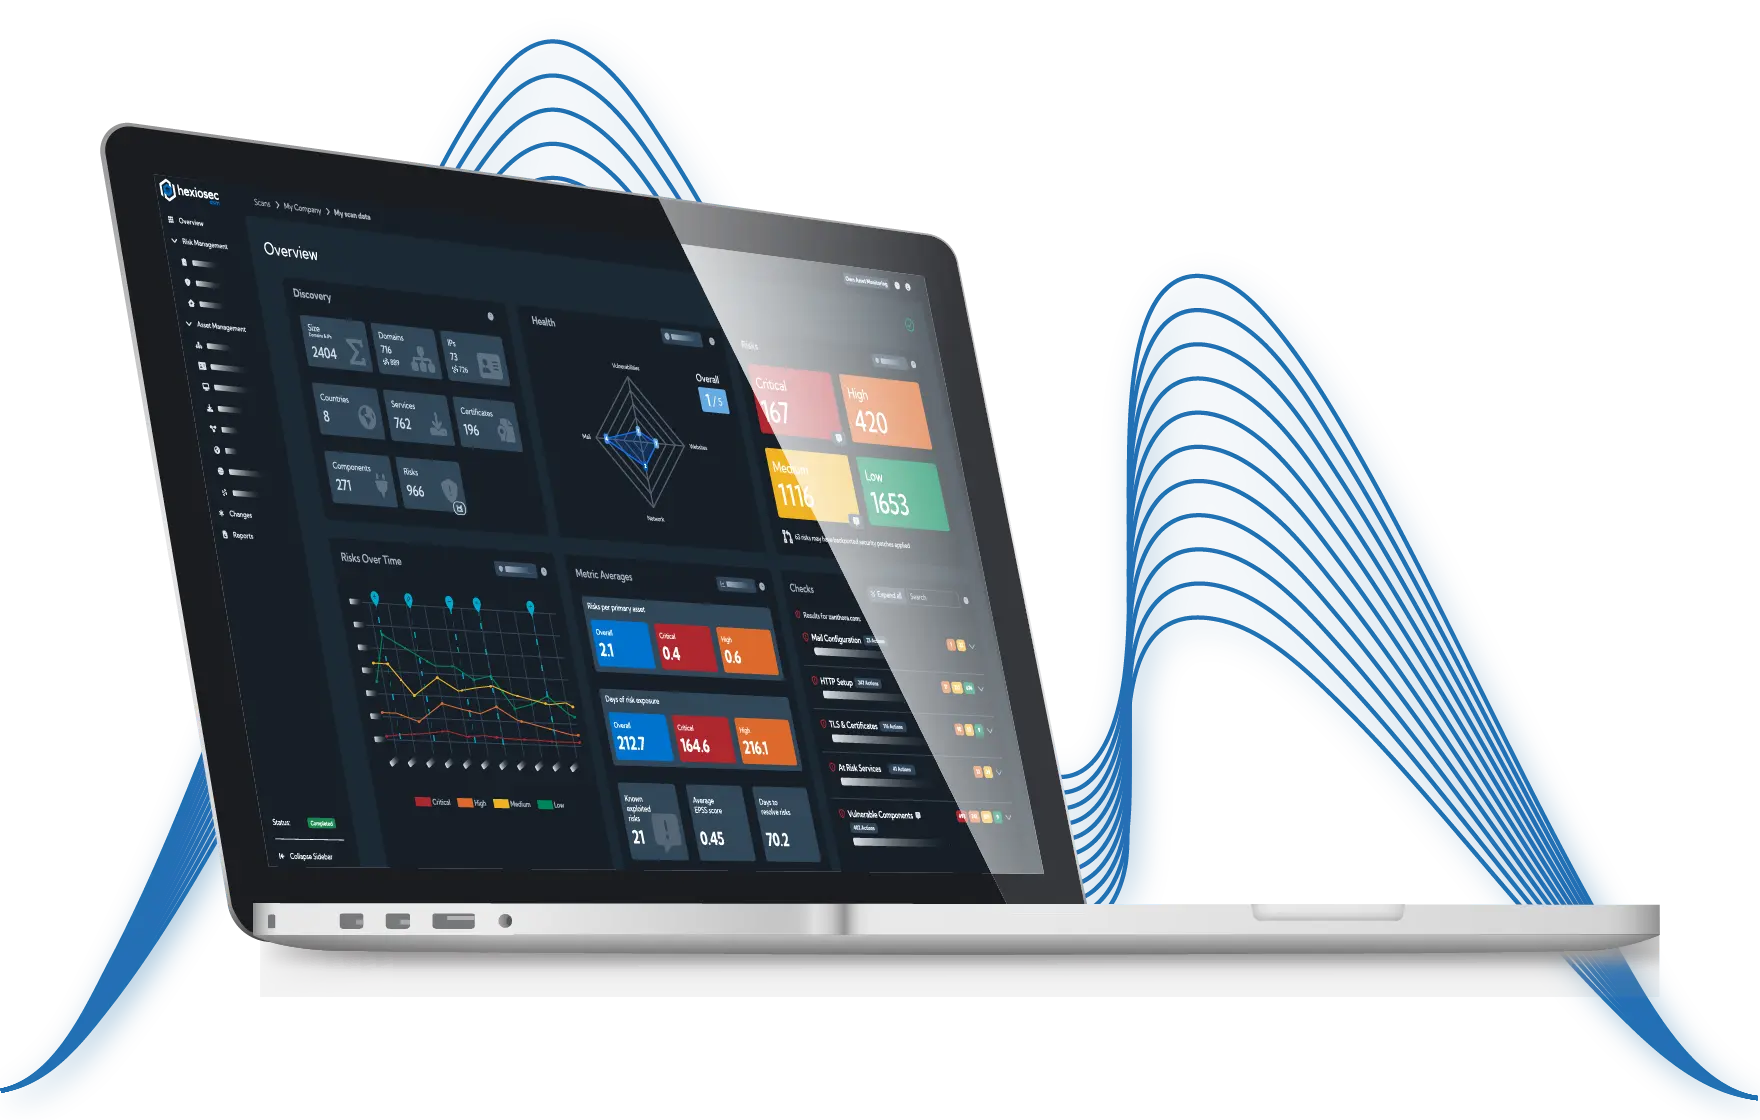
Reorganisations, mergers and departmental projects leave portals, sites and services running long after the teams behind them moved on. Hexiosec ASM maps the whole internet-facing estate from a single domain and ranks what to fix first.
Find the forgotten estate
Map portals, sites and services across merged and reorganised organisations.
Prioritise by exploitability
KEV and EPSS ranking so a stretched team works the genuinely urgent issues.
DSPT evidence
Maintain the asset and vulnerability evidence the toolkit asks for, continuously.
Monitor supplier exposure
Extend the same assessment to the suppliers holding patient data, starting with one supplier on a free account.
When the finding needs a person, not a patch
Some issues point at architecture, legacy dependency or governance rather than a missing update. Hexiosec Services works with healthcare teams on the parts a platform cannot fix on its own.
Remediation planning
A plan your team can resource around clinical priorities and change windows.
Legacy and migration support
Practical routes off end-of-life systems that cannot simply be switched off.
Architecture review
Where the same class of exposure keeps returning across the estate.
Governance and assurance
Process design so DSPT evidence stays current between submissions.
Evidence for the frameworks you answer to
The underlying asset and vulnerability data is the same. What changes is the format each submission wants it in.
DSPT
Asset and vulnerability evidence for the Data Security and Protection Toolkit.
Cyber Essentials
Supporting evidence for boundary, patching and configuration questions.
NIS2
Where your organisation falls in scope as an essential service.
Cyber insurance
External exposure evidence at renewal for a large and visible estate.
Hexiosec ASM is so easy to get going with, and a massive win for identifying vulnerabilities, and have them analysed in terms of risk so you can focus attention in the right area at the right time.
Find your tier on each product
A quick fit guide, not a pricing table. Each card routes to the full pricing.
Hexiosec Transfer
Which Transfer tier fits your organisation
- Single practices start on the free tier
- Most organisations need the paid tier for workspaces
- Higher volumes and research sharing sit above that
Hexiosec ASM
Which ASM tier fits your estate
- A small practice often fits inside 50 assets
- Premium covers 300 assets with daily monitoring
- Trusts and ICBs will need Enterprise scoping
Questions from healthcare teams
Does this help with DSPT?
Is patient data held in the UK?
Will scanning affect clinical systems?
Can we assess our suppliers?
Our estate came from several merged organisations. Can we separate it?
Do you work with private healthcare as well as the NHS?
Two risks, one supplier, one jurisdiction
Start with whichever is more pressing. Both are UK sovereign and built by the same engineers.