Evidence, not adjectives
You are considering giving a supplier a map of your weaknesses. This page sets out who we are, what we hold, how the platform actually works, and what we will put in writing.
- UK Sovereign
- NCSC ACD 2.0 Supplier
- UK sovereign
- Government Commercial Agency
- JOSCAR
- G‑Cloud 15
- DSIT Software Security Ambassador
What we hold, and what each one actually means
Certifications are only useful if you know what they cover. Here is the plain version.
ORGANISATION
Cyber Essentials Plus
An independently verified assessment of our own security controls as an organisation, including hands-on technical testing rather than self-assessment.
PRODUCT TRIAL
NCSC ACD 2.0 supplier
Hexiosec ASM was one of the suppliers chosen by the National Cyber Security Centre (NCSC) for its Active Cyber Defence (ACD) 2.0 trials, which contributed to the resulting external attack surface management (EASM) buyer’s guide.
PROCUREMENT
Government Commercial Agency
Available to buy through the Government Commercial Agency (GCA), which removes a procurement hurdle for public sector organisations.
SUPPLY CHAIN
JOSCAR registered
Supplier assurance for the aerospace, defence and security sector, which matters if you sit in a defence supply chain. JOSCAR is the Joint Supply Chain Accreditation Register.
COMMITMENT
DSIT Software Security Ambassador
We support the UK government code of practice for software vendors, published by the Department for Science, Innovation and Technology (DSIT), and we build to it rather than just referencing it.
FRAMEWORK
G‑Cloud 15
Hexiosec ASM is listed on G‑Cloud 15, so public sector buyers can purchase through a framework they already hold rather than running a separate procurement exercise.
Chosen for the trials that shaped UK guidance
Hexiosec ASM was one of the suppliers chosen by the National Cyber Security Centre (NCSC) for its Active Cyber Defence (ACD) 2.0 trials, which contributed to the resulting external attack surface management (EASM) buyer’s guide. The trials validated external attack surface management as a security practice and deemed it essential for effective cyber defence. The guide helps buyers assess the category on its merits rather than on vendor claims.
- Selected as a supplier for the ACD 2.0 trials
- Contributed to the resulting EASM buyer’s guide
- The trials validated EASM as a practice, not one product
- Read the guide and assess us against it
British built, British hosted, British operated
Hexiosec is a UK company based in Cheltenham, founded by engineers from UK government, defence and intelligence backgrounds. The platform runs on UK infrastructure and your estate data does not leave the country. For public sector, legal and financial buyers, this is usually the first question and the one that decides whether a tool can be bought at all.
- Designed, built and operated in the United Kingdom
- Estate data stored and processed in the UK
- A UK company, subject to UK law
- Support from the people who built the product
Non-intrusive by design, so nothing has to be taken offline
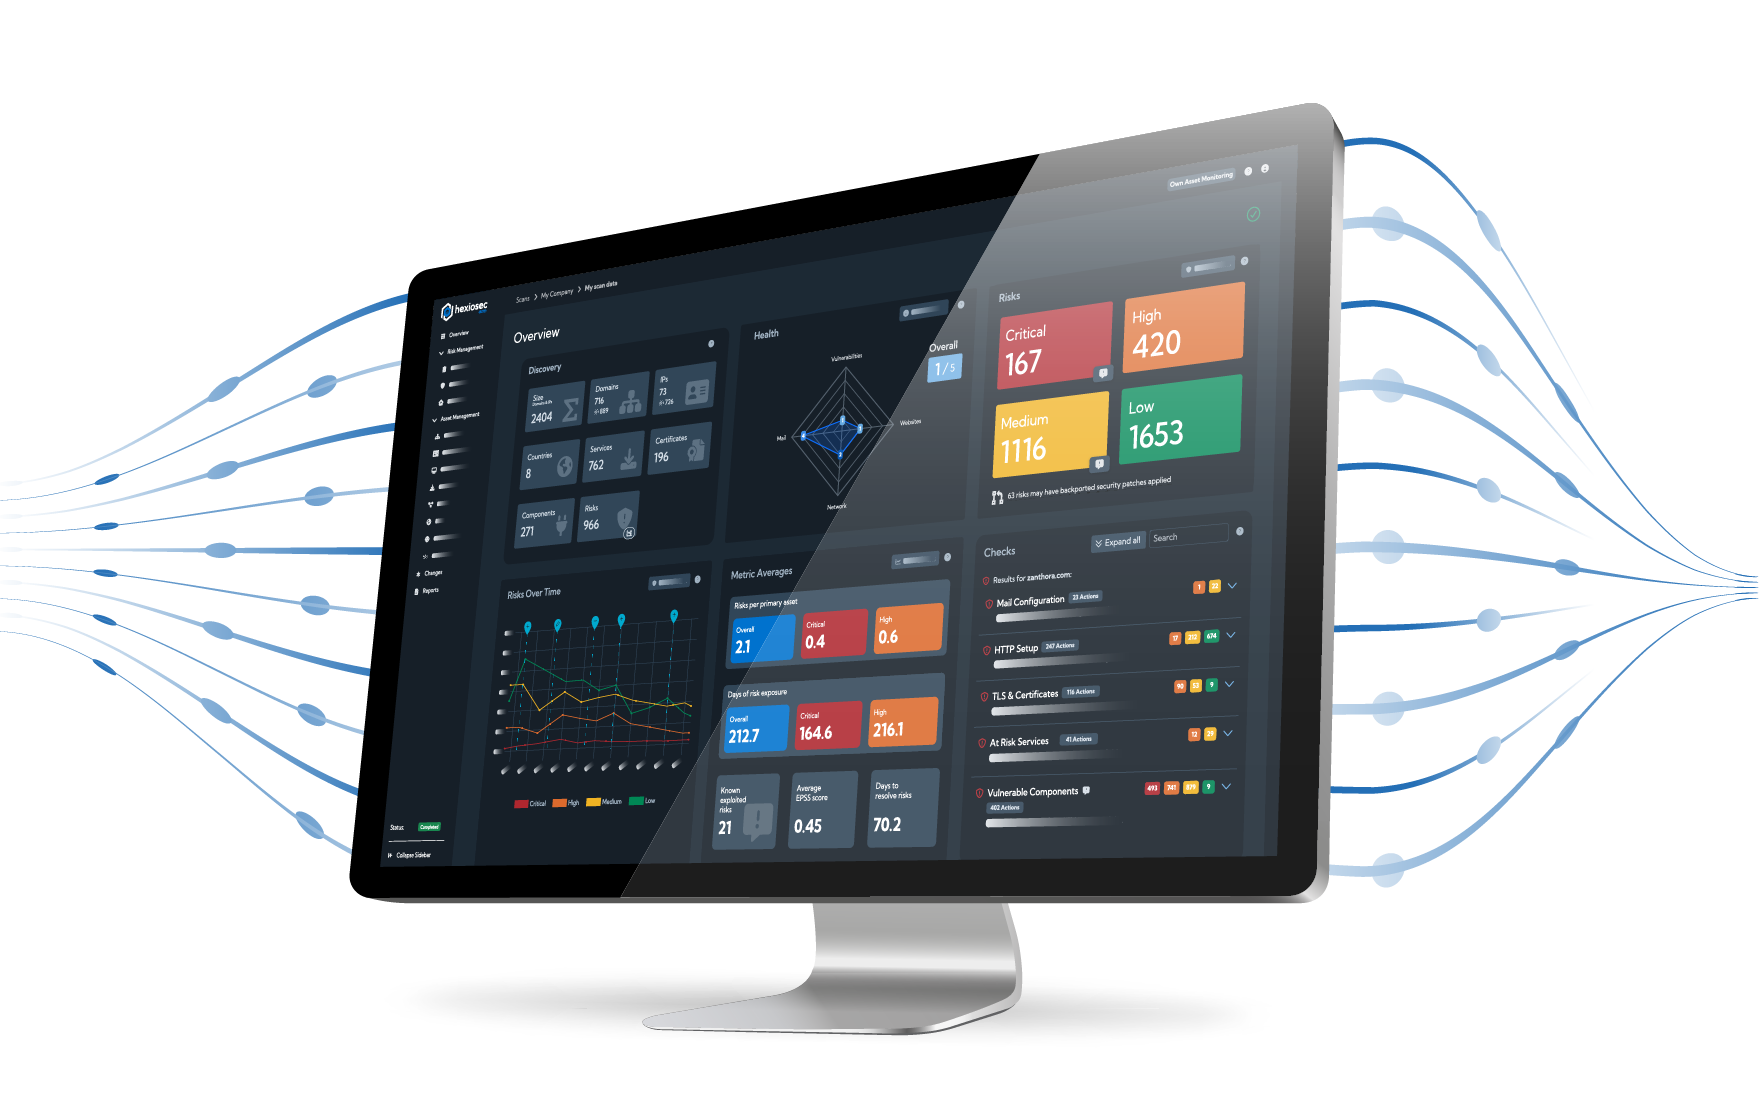
Hexiosec ASM assesses exposure using publicly available information: DNS records, certificate transparency logs, routing data and what services voluntarily disclose about themselves. We do not exploit, brute force, or send traffic intended to test a weakness. That is what makes it safe to run against your own estate without a change window.
- No exploitation, no brute forcing, no interference
- Nothing sent that could disrupt a production service
- Nothing installed, and no change window required
- The same method whether the estate is yours or a supplier’s
How we handle what we find
Everything we discover about your estate is sensitive. These are the controls around it.
UK data residency
Estate data is stored and processed in Google Cloud’s London data centres, the same UK infrastructure Hexiosec Transfer runs on. It is not replicated outside the United Kingdom.
Least privilege by default
Where you connect a cloud account, access is read-only and scoped to inventory metadata. We cannot change anything in your environment.
Access control and separation
Customer data is separated, and internal access is limited to the people who need it to support you.
Audit logging
Platform and connector activity is logged, so you can see what was done and when.
Encryption in transit and at rest
Your estate data is encrypted both in transit and where it is stored.
Documentation and questionnaires
We complete your security questionnaire, share our published procurement documents, and answer specific technical questions in writing.
Evidence for the frameworks you answer to
Hexiosec ASM produces asset and vulnerability evidence that sits behind several UK and EU frameworks. The detail for each one is covered on our compliance page.
NCSC CAF
Asset management and vulnerability evidence for Cyber Assessment Framework (CAF) outcomes and GovAssure submissions.
NIS2
Visibility and risk management duties under the second Network and Information Systems Directive (NIS2) for in-scope operators and their supply chains.
DORA
Information and communication technology (ICT) risk management and third-party oversight duties under the Digital Operational Resilience Act (DORA) for financial entities.
DSPT
Asset and vulnerability evidence for the Data Security and Protection Toolkit (DSPT), for health and care organisations.
Cyber Essentials
Supporting evidence for the boundary and patching questions in the assessment.
Lexcel and client audits
Evidence for law firms answering client due diligence and panel requirements.
We publish a disclosure route, and we use it
Security questionnaires ask whether a supplier has a vulnerability disclosure process. Ours is published, staffed and linked below, rather than described in a policy nobody can find.
Tell us directly
Report it to our security team with the detail. We will acknowledge it, keep you updated, and tell you what we did about it.
We will not come after you
Good faith research reported responsibly is welcome. We are engineers and we would want the same treatment.
The questions security teams actually ask
Which frameworks can we buy you through?
Where is our data held?
Do you need credentials for our systems?
Could scanning disrupt our services?
Is it legal to scan a supplier?
Will you complete our security questionnaire?
Who owns the data you produce about our estate?
Ask us the hard questions
We will answer them in writing, and put you in touch with the engineers who built it.