CLOUD CONNECTOR
The exposed resource nothing points at is still yours
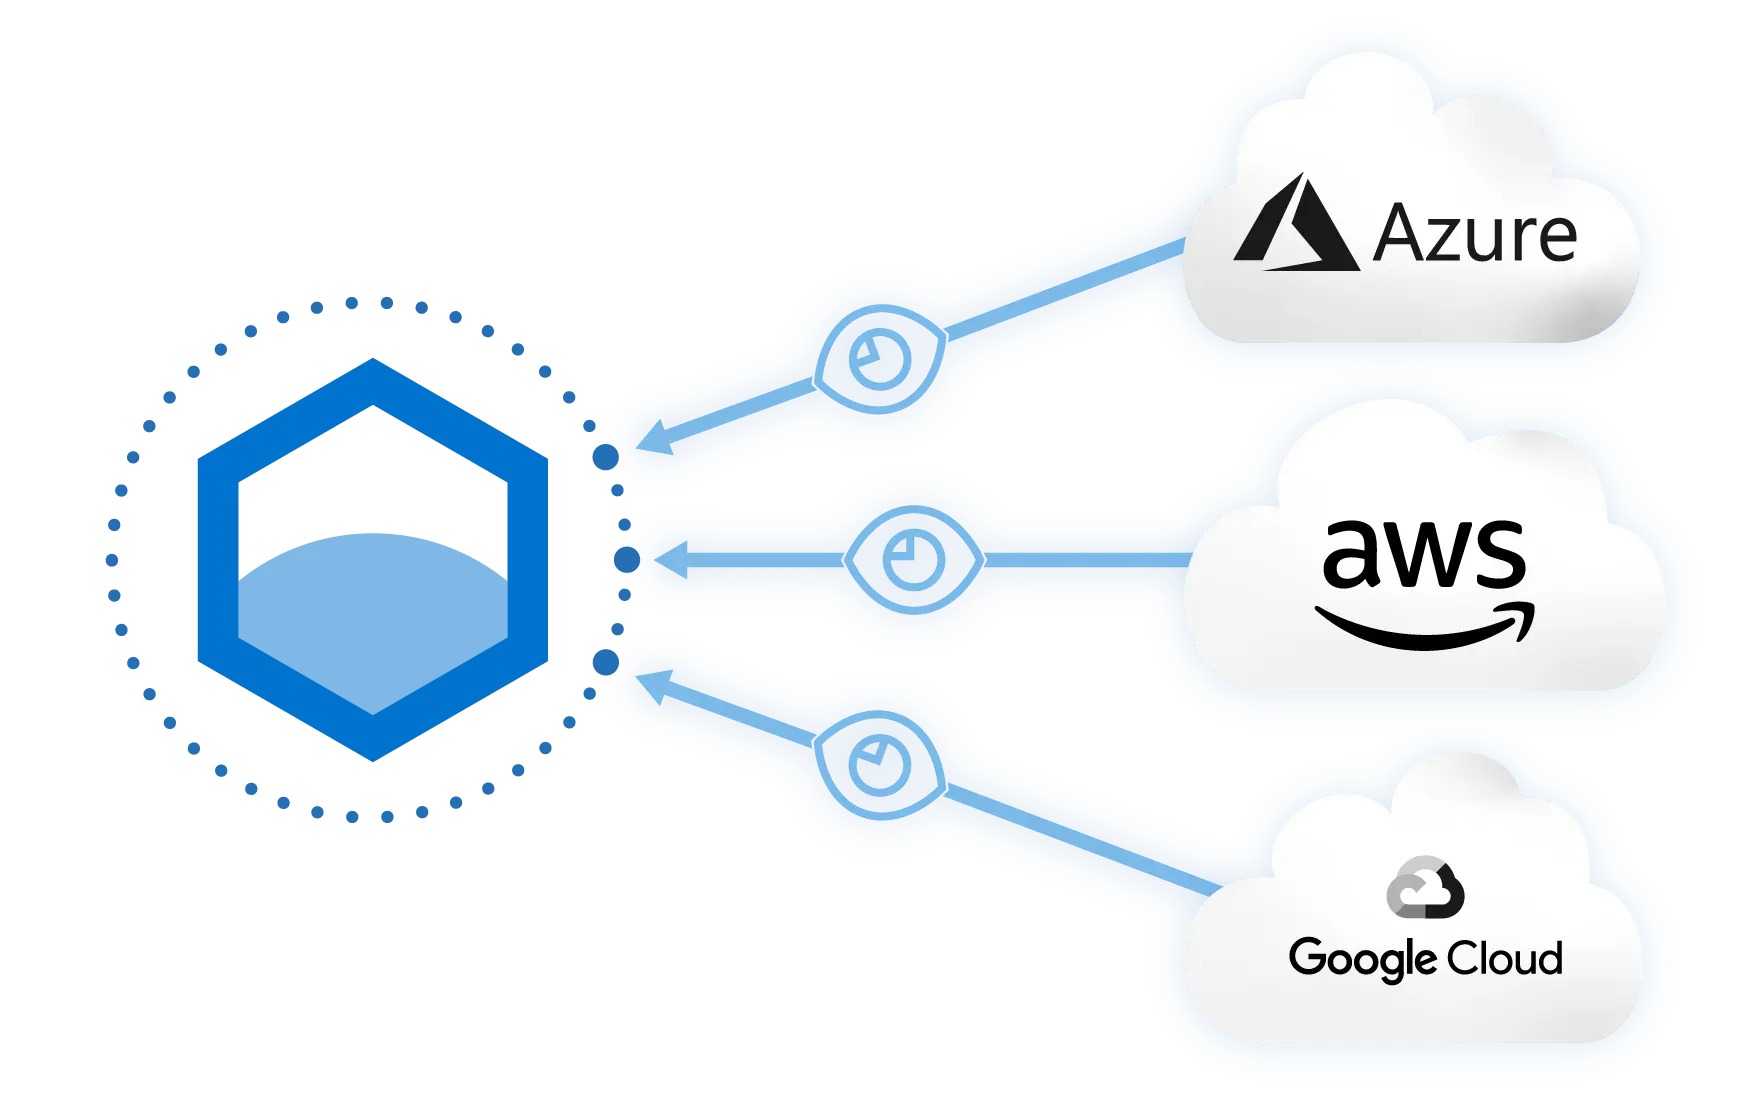
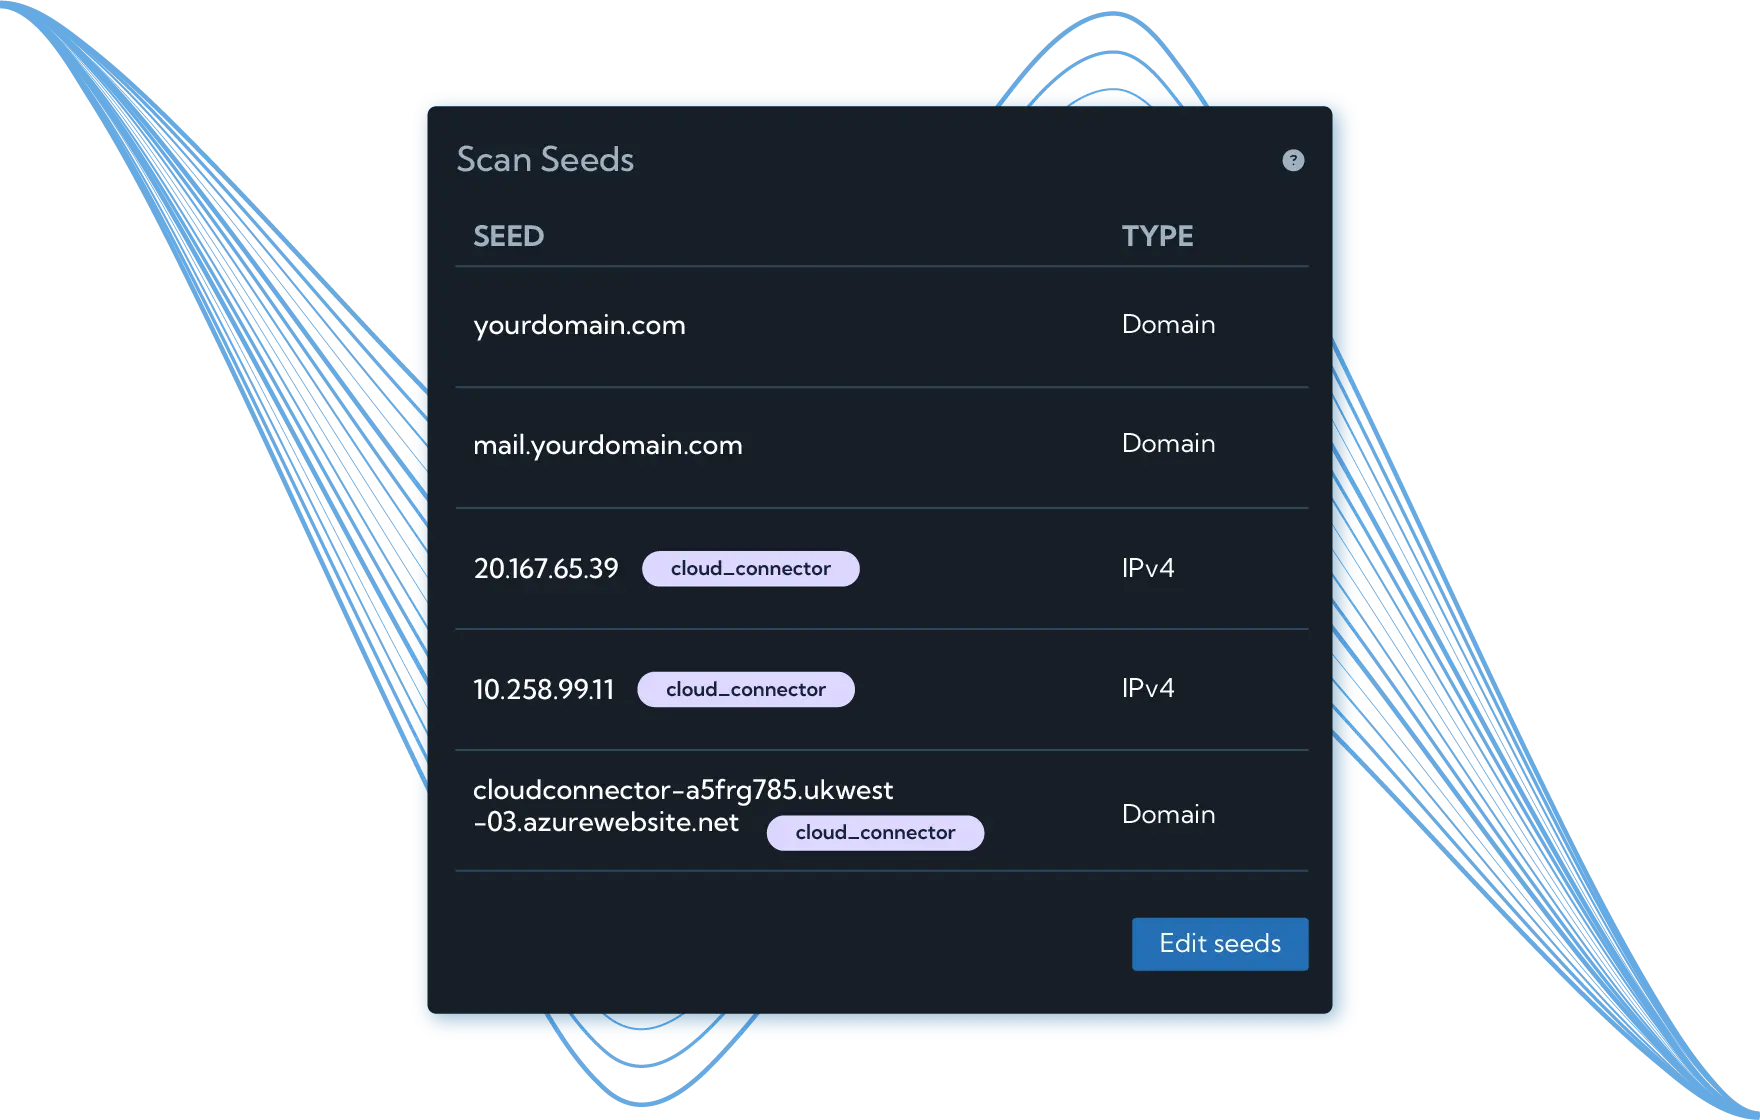
External discovery finds what the internet can attribute to you. The Cloud Connector adds a read-only view of your AWS, Azure and Google Cloud accounts, so public resources with no obvious link back to your brand are still accounted for.
- Read-only access
- Least privilege
- Controlled by you
Close the gap between deployed and discoverable
Cloud estates create exposure faster than any documentation process can record it, and much of it carries nothing that ties it to your organisation.
NO BLIND SPOTS
Find public resources that nothing links to you
A storage bucket or load balancer with no branding or custom domain is still your incident when it goes wrong.
FASTER FIXES
Route issues to the team that owns the account
Account and resource context means remediation goes to the right engineer instead of around the houses.
INTEGRATE SAFELY
Bring an acquired cloud estate under control
Connect the accounts you have just inherited and see what they expose before the integration work starts.
PROVE CONTROL
Evidence cloud asset management
Show auditors that cloud resources are inventoried and monitored, not assumed to be covered.
For teams running cloud faster than they can document what’s in it
The platform or cloud engineer
You know what should be public. You need to know what actually is, across every account and subscription.
The security lead with multi-account sprawl
Self-service teams, several providers and no single view of what is exposed where.
The IT lead post-migration
Things moved. You need to confirm that what was meant to be private ended up private.
Associating resources with your organisation isn’t always obvious
Short-lived infrastructure, multiple accounts and self-service teams mean public resources appear constantly, often with nothing linking them back to a domain you monitor.
Assets with no obvious owner
A public endpoint may carry no name, certificate or record that ties it to your organisation.
Multiple accounts, multiple teams
Estates sprawl across accounts, subscriptions and projects with different owners and standards.
Change is constant
What is exposed this morning may not be what was exposed last night, and nobody filed a ticket.
Read-only by design
Connect an account with least-privilege, read-only credentials. Hexiosec ASM never makes changes to your cloud environment, and connector activity is logged for your own review.
- Read-only, least-privilege access
- Support for AWS, Azure and Google Cloud
- Multiple accounts, subscriptions and projects
- Full audit logging of connector activity
Inside-out meets outside-in
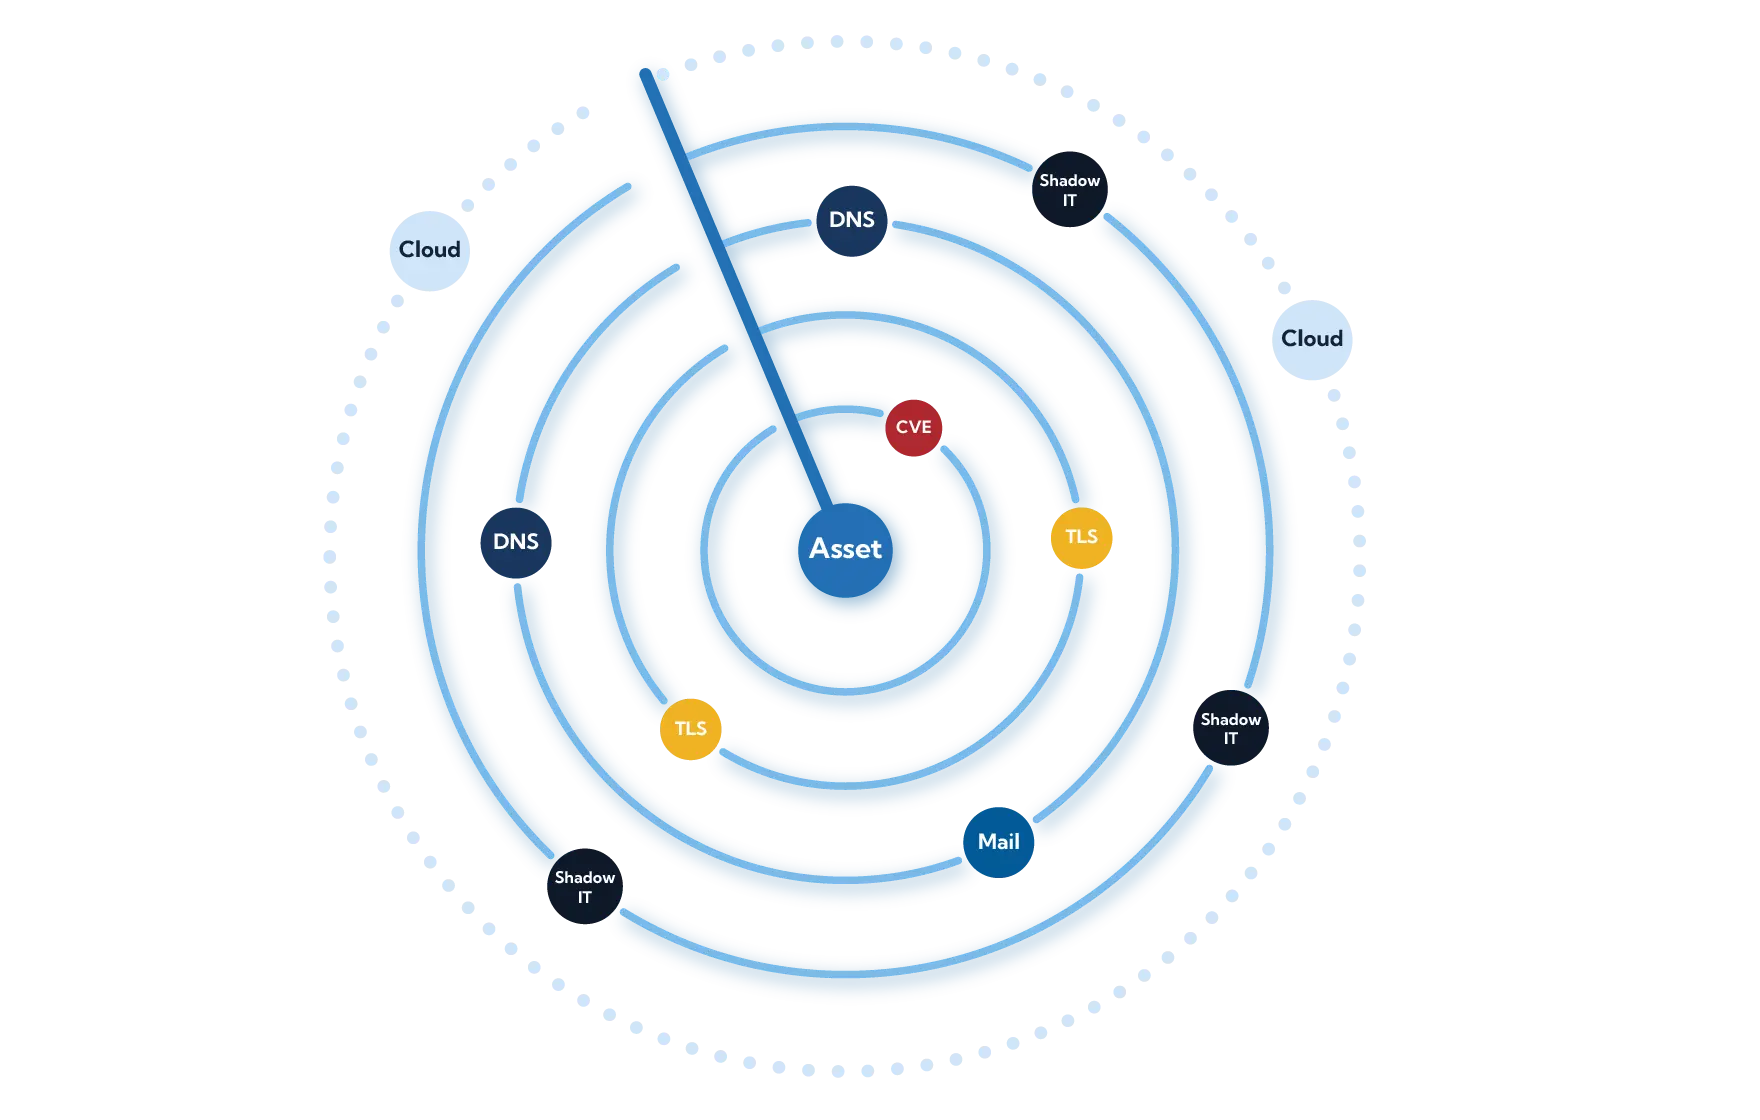
Cloud inventory is reconciled with what external discovery already found, so you can see which resources are exposed, which are accounted for, and which nobody expected to be public.
- Public resources matched to discovered assets
- Exposed resources with no external footprint
- Account and ownership context on every asset
- Gaps highlighted rather than buried
Keep pace with the estate
The connector refreshes on your schedule, so newly exposed resources are picked up as part of the same continuous view rather than waiting for the next manual review.
- Scheduled refresh of cloud inventory
- New exposure surfaced automatically
- Consistent risk scoring across cloud and external assets
- One inventory, whatever the source
What the connector does and does not do
We read inventory metadata, nothing else.
Read-only, always
The connector has no write permissions. It cannot change, create or delete anything in your environment.
Inventory metadata only
We read resource configuration and exposure metadata. We do not read the contents of your storage, databases or workloads.
Least privilege
Permissions are scoped to the minimum required, so your cloud team can review exactly what is granted before approving.
Audit logged
Connector activity is logged, and it appears in your own provider audit trail.
Multiple providers
AWS, Azure and Google Cloud, across as many accounts, subscriptions or projects as you need.
Optional, not required
External discovery works without it. The connector adds depth for teams that want the inside-out view too.
Where the inside-out view matters most
The connector is technical, but the reasons for turning it on are usually not.
asm led
Achieve compliance
Evidence that cloud assets are inventoried and monitored, not assumed to be in scope.
ASM + Services
M&A due diligence
Assess an acquired cloud estate quickly, from both directions.
ASM + Services
Digital transformation
Give a migration a verified before and after rather than a hopeful one.
ASM Led
Cyber insurance readiness
Reduce the chance that an unknown public resource becomes the claim.
When the answer is architecture, not a checkbox
If the connector keeps surfacing the same class of exposure, the problem is usually structural. Our consultants work with teams on the design and governance underneath, so the same issues stop reappearing every quarter.
- Cloud and infrastructure architecture review
- Migration planning and hardening for legacy services
- Guardrails and governance so self-service teams stay inside the lines
- Practical remediation planning with the people who own the accounts
Hexiosec ASM gives us clear, real‑time visibility of our external attack surface and highlights risks we simply couldn’t see before. It’s helped us close gaps long before they could become incidents.

Cloud Connector availability
The connector comes in with API access on Enterprise. External discovery runs on every tier without it.
Not included
External discovery only. Public cloud resources are still found wherever they can be attributed to you.
Not included
External discovery across up to 300 assets, with daily monitoring. The connector is an Enterprise capability.
Included with API access
Multi-account coverage across AWS, Azure and Google Cloud, with estate-wide scoping.
Questions your cloud team will ask
What permissions does it need?
Can it change anything in our environment?
Do you read our data?
Which providers are supported?
What if we cannot connect an account?
How often does it refresh?
Bring your cloud into view
Book a demo and we will walk your team through the permissions model before anything is connected.