Cyber Security for the Defence Supply Chain
Cyber requirements flow down the defence supply chain, and the organisations awarding you work increasingly check what you expose before they ask. Hexiosec ASM shows you what they will find. Hexiosec Transfer secures the technical data you exchange with them.
- UK Sovereign
- Cyber Essentials Plus
- JOSCAR registered
- NCSC ACD 2.0 (ASM)
- Built by ex-defence engineers
Same contract. Two directions of risk.
Transfer
The data you exchange
Technical documentation, drawings, specifications and tender material moving between you, primes and the wider supply chain.
- Technical data and drawings
- Tender and bid documentation
- Subcontractor exchange
- Assurance evidence for primes
asm
The estate they assess
Your internet-facing infrastructure, which a prime or an adversary can survey without asking you anything at all.
- Company sites and portals
- Legacy infrastructure from earlier contracts
- End-of-life software still exposed
- Subcontractors carrying your data
Same contract. Two directions of risk. Hexiosec covers both.
Two products, one supply chain. Start where your risk is.
Hexiosec Transfer: Secure the data you exchange
Encrypted exchange and controlled workspaces for technical documentation, tenders and assurance evidence.
Hexiosec ASM: See what your primes see
Continuous external discovery, so you find your own exposure before it appears in someone else's assessment.
Technical data should not move by email
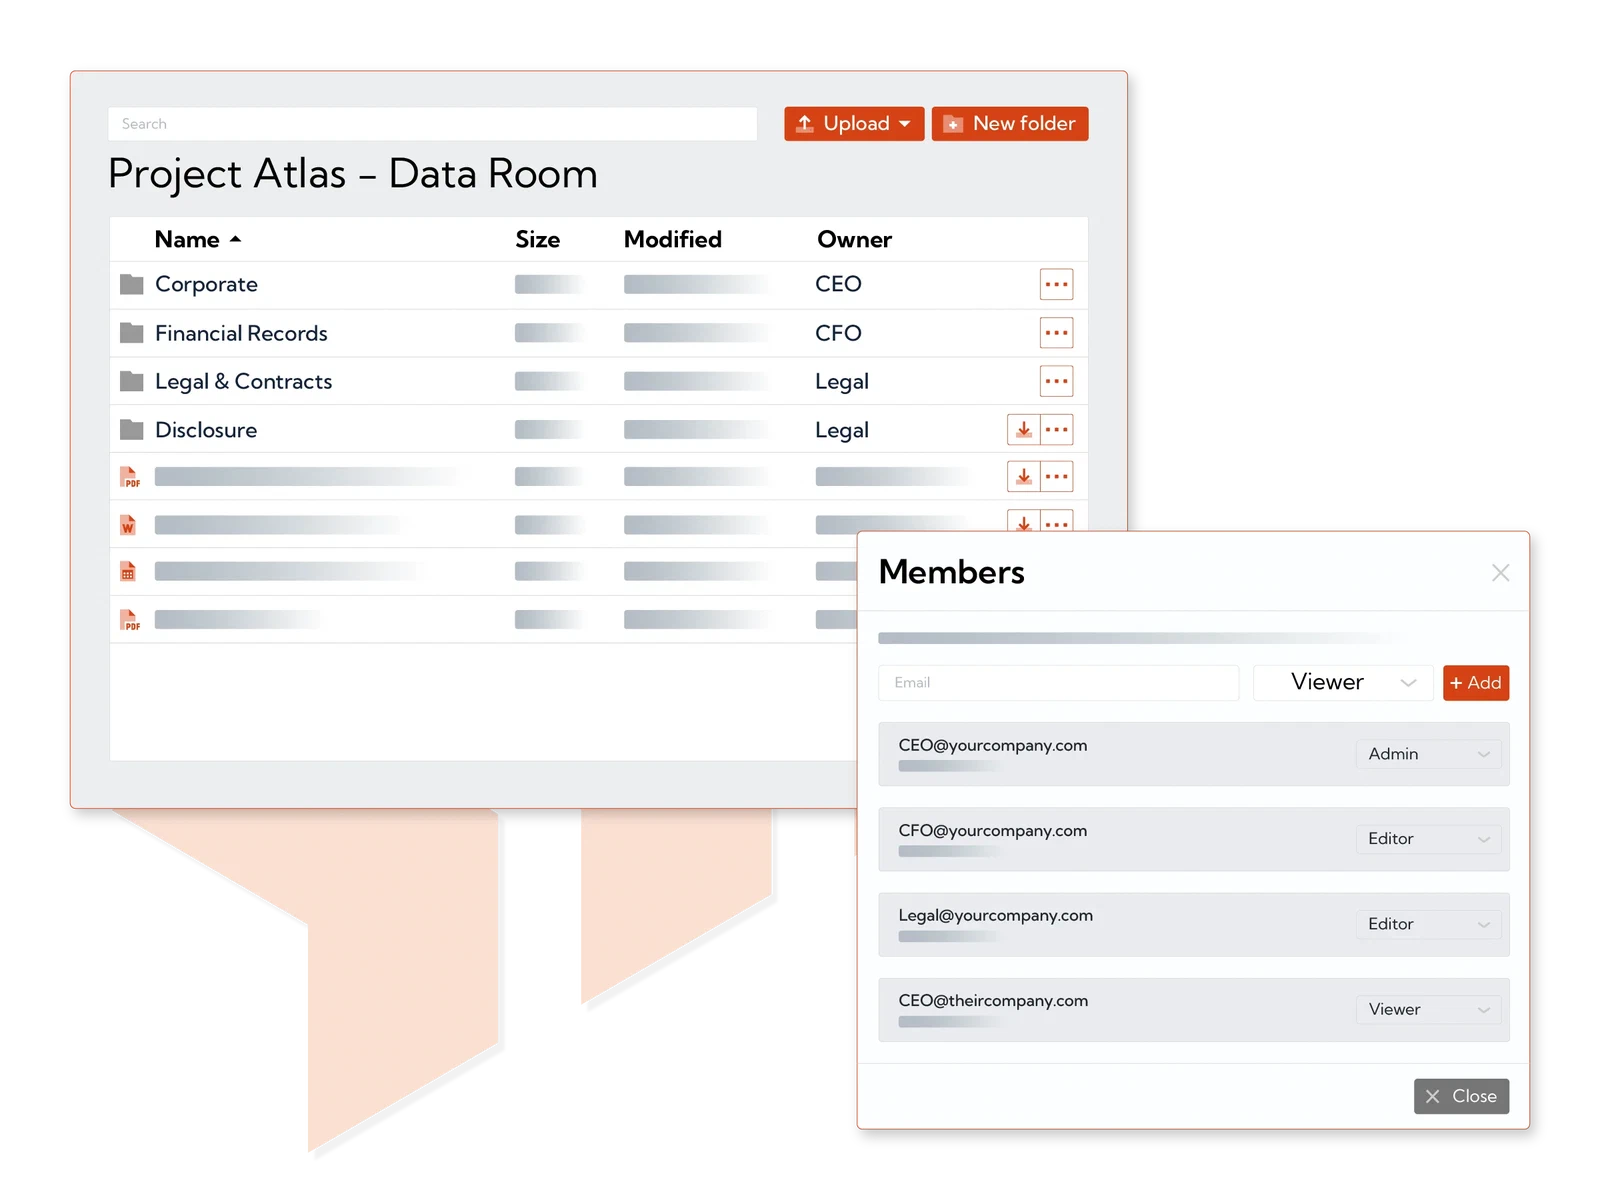
Drawings, specifications and tender material are exactly what an adversary wants and exactly what primes expect you to protect. Hexiosec Transfer provides encrypted exchange and controlled workspaces, hosted and operated in the UK.
Technical documentation
Send drawings and specifications with end-to-end encryption, controlled access and an audit trail.
Tender and bid material
Exchange commercially sensitive documentation without consumer file services.
Subcontractor exchange
Give each relationship a controlled space with access that ends with the work.
Assurance evidence
Provide certifications and evidence to primes through an auditable channel.
Find it before your prime does
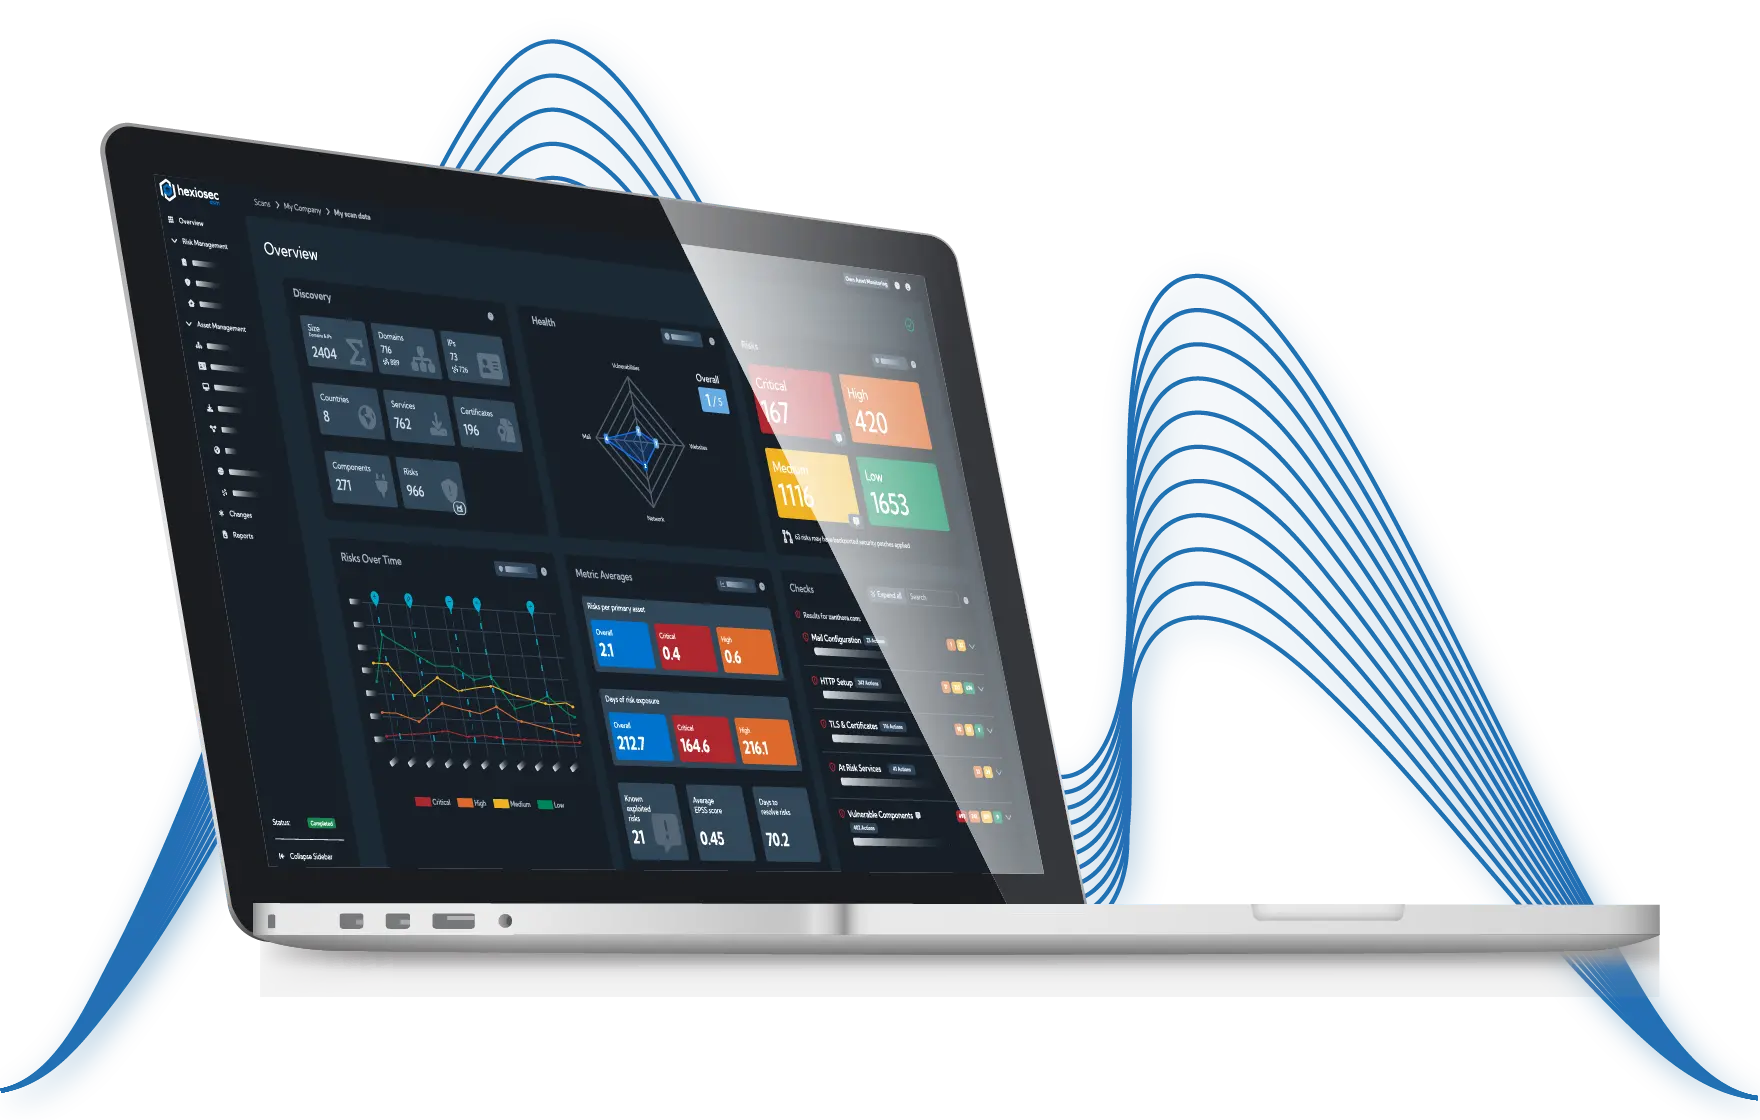
Cyber requirements now flow down the supply chain, and assessment increasingly starts with what is publicly visible. Hexiosec ASM gives you the same outside-in view, so you can fix things on your own timetable rather than in response to a question.
See what assessors see
Map your internet-facing estate the way a prime or an adversary would.
Prioritise by exploitability
Known Exploited Vulnerabilities (KEV) and Exploit Prediction Scoring System (EPSS) ranking so a small team fixes the things that matter first.
Evidence your controls
Maintain asset and vulnerability evidence for assurance questions and audits.
Watch your own suppliers
Extend assessment down to the subcontractors carrying your data, starting with one supplier on a free account.
Requirements that need engineering, not paperwork
Flow-down requirements often land on organisations without a security function. Hexiosec Services is staffed by engineers from UK defence and intelligence backgrounds who have worked to these expectations themselves.
Readiness and gap work
Understand what is actually required of you and what it will take to meet it.
Remediation planning
A plan proportionate to your size and the contracts you are pursuing.
Architecture and hardening
Practical engineering support for legacy manufacturing and design environments.
Governance and evidence
Process that keeps assurance evidence current between assessments.
What flows down to you
Requirements vary by prime and by contract. These are the ones we are asked about most, and our guides set out what the evidence looks like in practice.
JOSCAR
Supplier assurance registration for aerospace, defence and security.
Cyber Essentials and Plus
Commonly required in defence contracting, and a frequent flow-down condition.
Prime flow-down requirements
Contractual cyber conditions passed down from the primes you supply.
Supplier oversight
Your own subcontractors, assessed on the same basis.
Grey Zone Services use Hexiosec's Attack Surface Management tool which is excellent. Simple to use, stacked with features and will tell you more about your own company and your supply chain's vulnerabilities than you could ever wish for. Great work Hexiosec, an impressive capability
Find your tier on each product
A quick fit guide, not a pricing table. Each card routes to the full pricing.
Hexiosec Transfer
Which Transfer tier fits your organisation
- Smaller suppliers start on the free tier
- Most need the paid tier for controlled workspaces
- Programme level exchange sits above that
Hexiosec ASM
Which ASM tier fits your estate
- Many smaller suppliers fit inside 50 assets
- Premium covers 300 assets with daily monitoring
- Group structures and subcontractor oversight need Enterprise
Questions from defence suppliers
We are a small supplier with no security team. Is this for us?
Which requirements apply to us?
Is our data held in the UK?
Can a prime see that we use this?
Can we assess our own sub-contractors?
Do you hold JOSCAR yourselves?
Two risks, one supplier, one jurisdiction
Start with whichever is more pressing. Both are UK sovereign and built by engineers from the same community you supply.