SUPPLY CHAIN MONITORING
Supply chain monitoring across your third parties
Your suppliers' exposure is your exposure. Monitor the external attack surface of the third parties who host, process or connect to your data, continuously and without needing their co-operation.
- No supplier co-operation needed
- Continuous, not annual
- Evidence for your framework
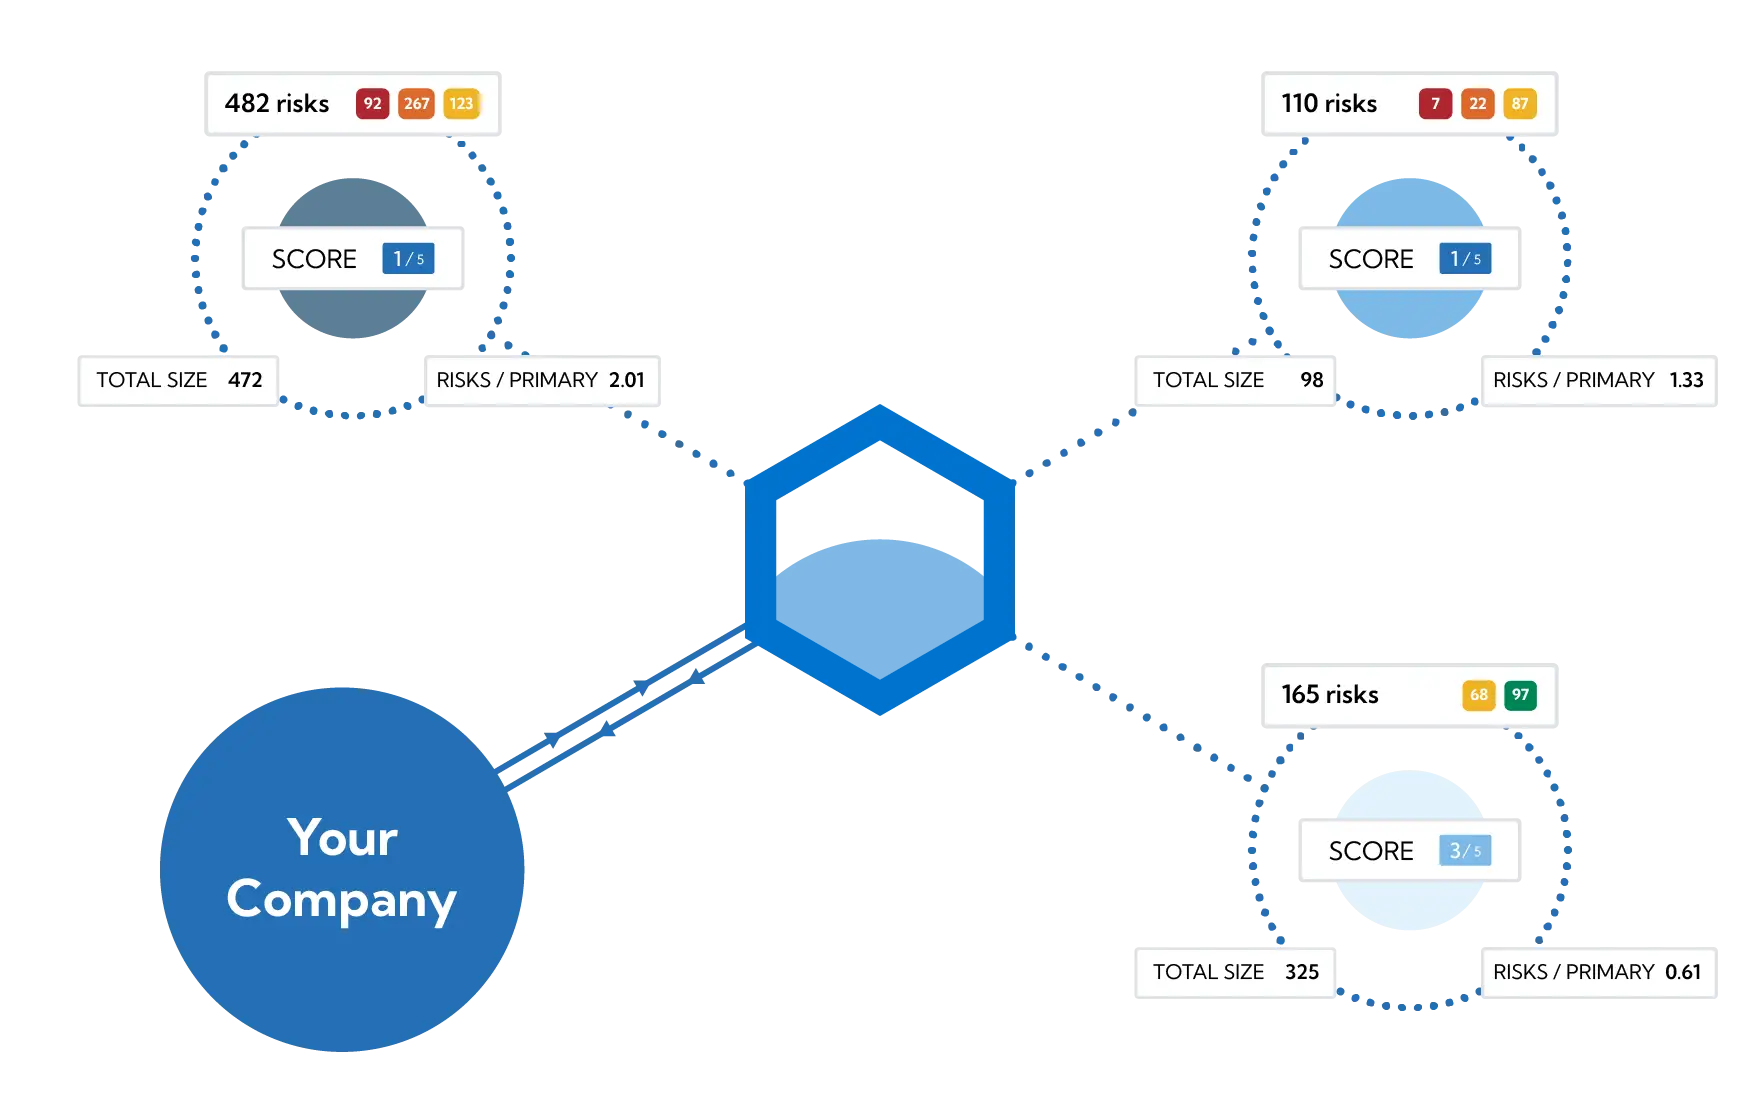
Replace an annual belief with a continuous fact
Third-party risk sits with your board and your regulator, but most assurance still runs on a self assessment somebody filled in last year.
CONTINUOUS ASSURANCE
Know a supplier is exposed before they tell you
Questionnaires describe intent. Monitoring shows the estate as it is today, including the things nobody thought to mention.
MEET YOUR DUTIES
Evidence third-party oversight to a regulator
DORA, CAF and NIS2 all place duties on how you oversee suppliers. Show a repeatable process rather than a filing cabinet.
NEGOTIATE BETTER
Go into renewal knowing what you are buying
Objective posture data changes the tone of a contract conversation and gives you something specific to ask for.
ACQUIRE SAFELY
See the suppliers you inherit in a transaction
A target brings its own supply chain. Map it before completion rather than discovering it afterwards.
For the people who carry third-party risk
The vendor or procurement risk lead
You run the assessment cycle and know a questionnaire is a snapshot of what someone was willing to write down.
The CISO with regulatory duties
DORA or CAF puts named responsibility on you for oversight of critical suppliers.
The IT lead in a supplier-heavy estate
Most of your service is delivered by other people. Their exposure lands on your incident bridge.
Questionnaires tell you what a supplier believed last year
Annual self assessment is the default control in most supply chain security programmes, and it is the weakest evidence in the file.
Attackers use the weakest link
Your data is only as protected as the smallest supplier holding a copy of it.
Point in time is not enough
A clean assessment in January says nothing about an exposed service in June.
Regulators expect oversight
DORA, CAF and NIS2 all ask how you monitor third parties, not just how you onboard them.
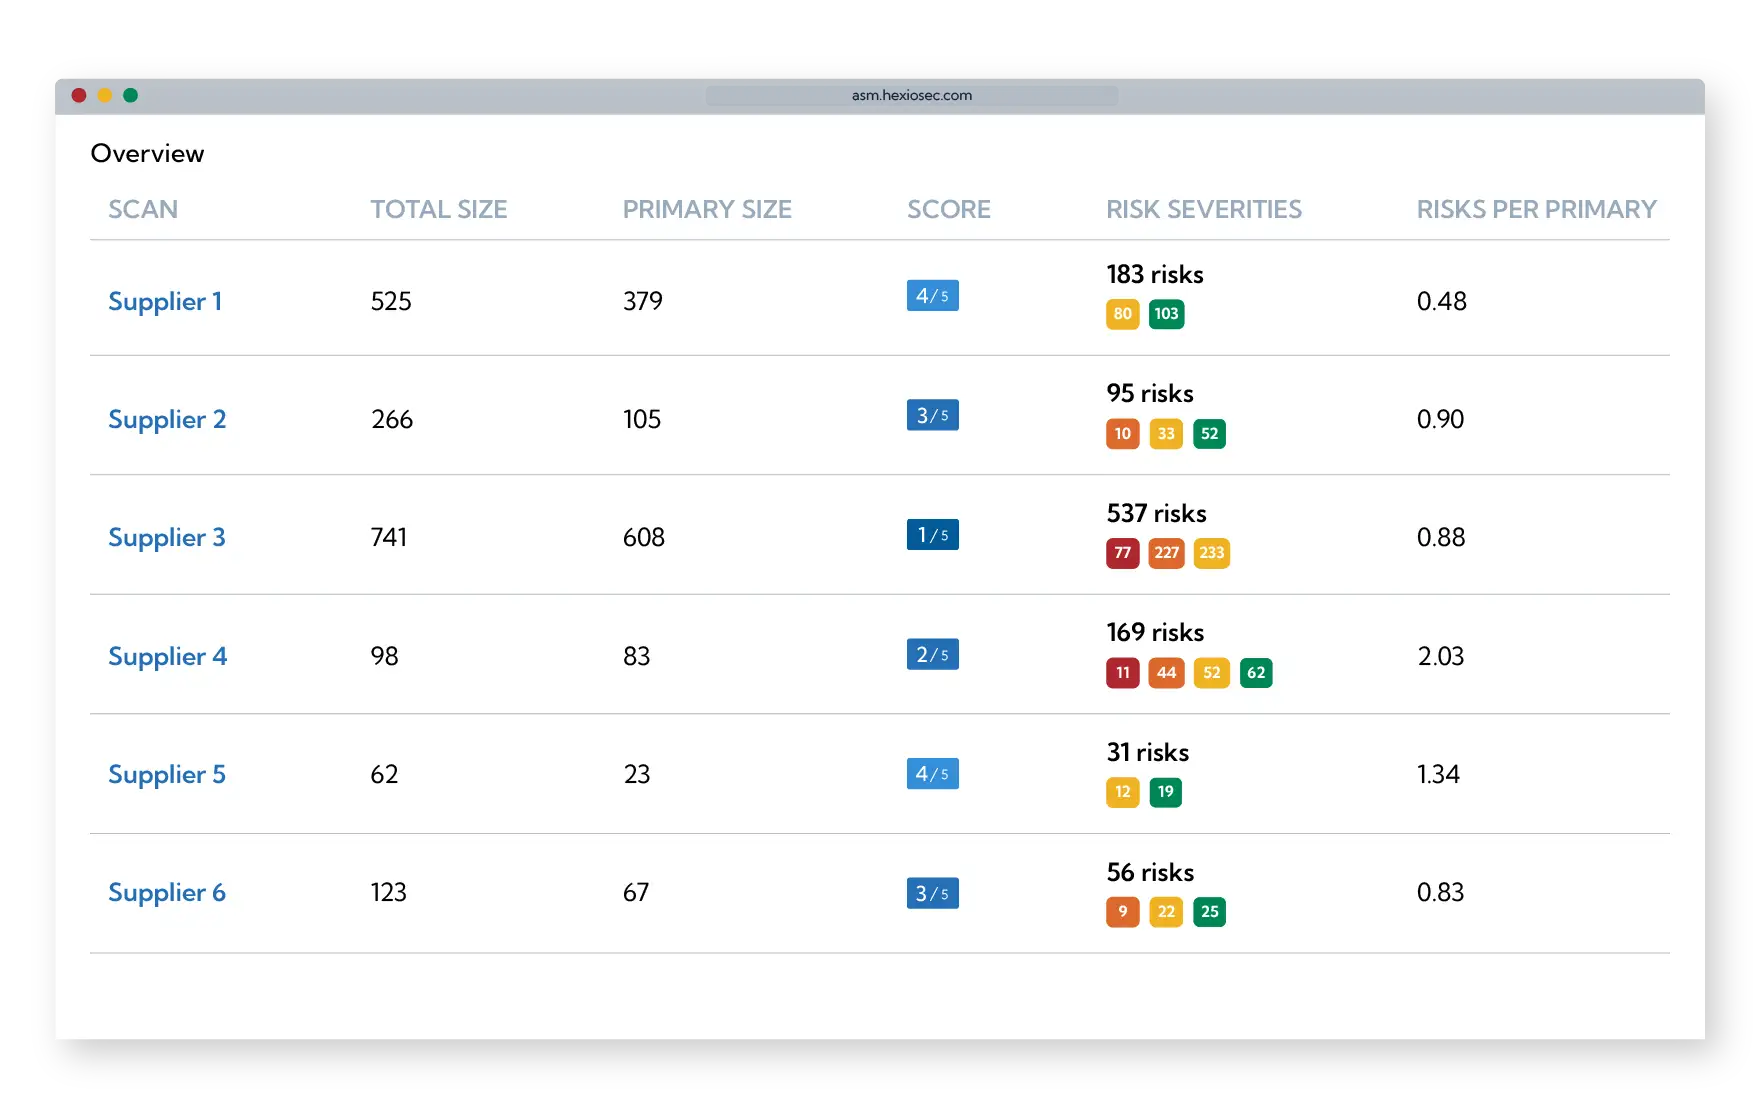
Every supplier, side by side
Add the suppliers that matter and see their external posture in one place, with comparable metrics rather than a number you cannot interrogate.
- Supplier dashboard with comparable metrics
- Side-by-side posture comparison
- Grouping by criticality or contract
- Trend over time as suppliers change
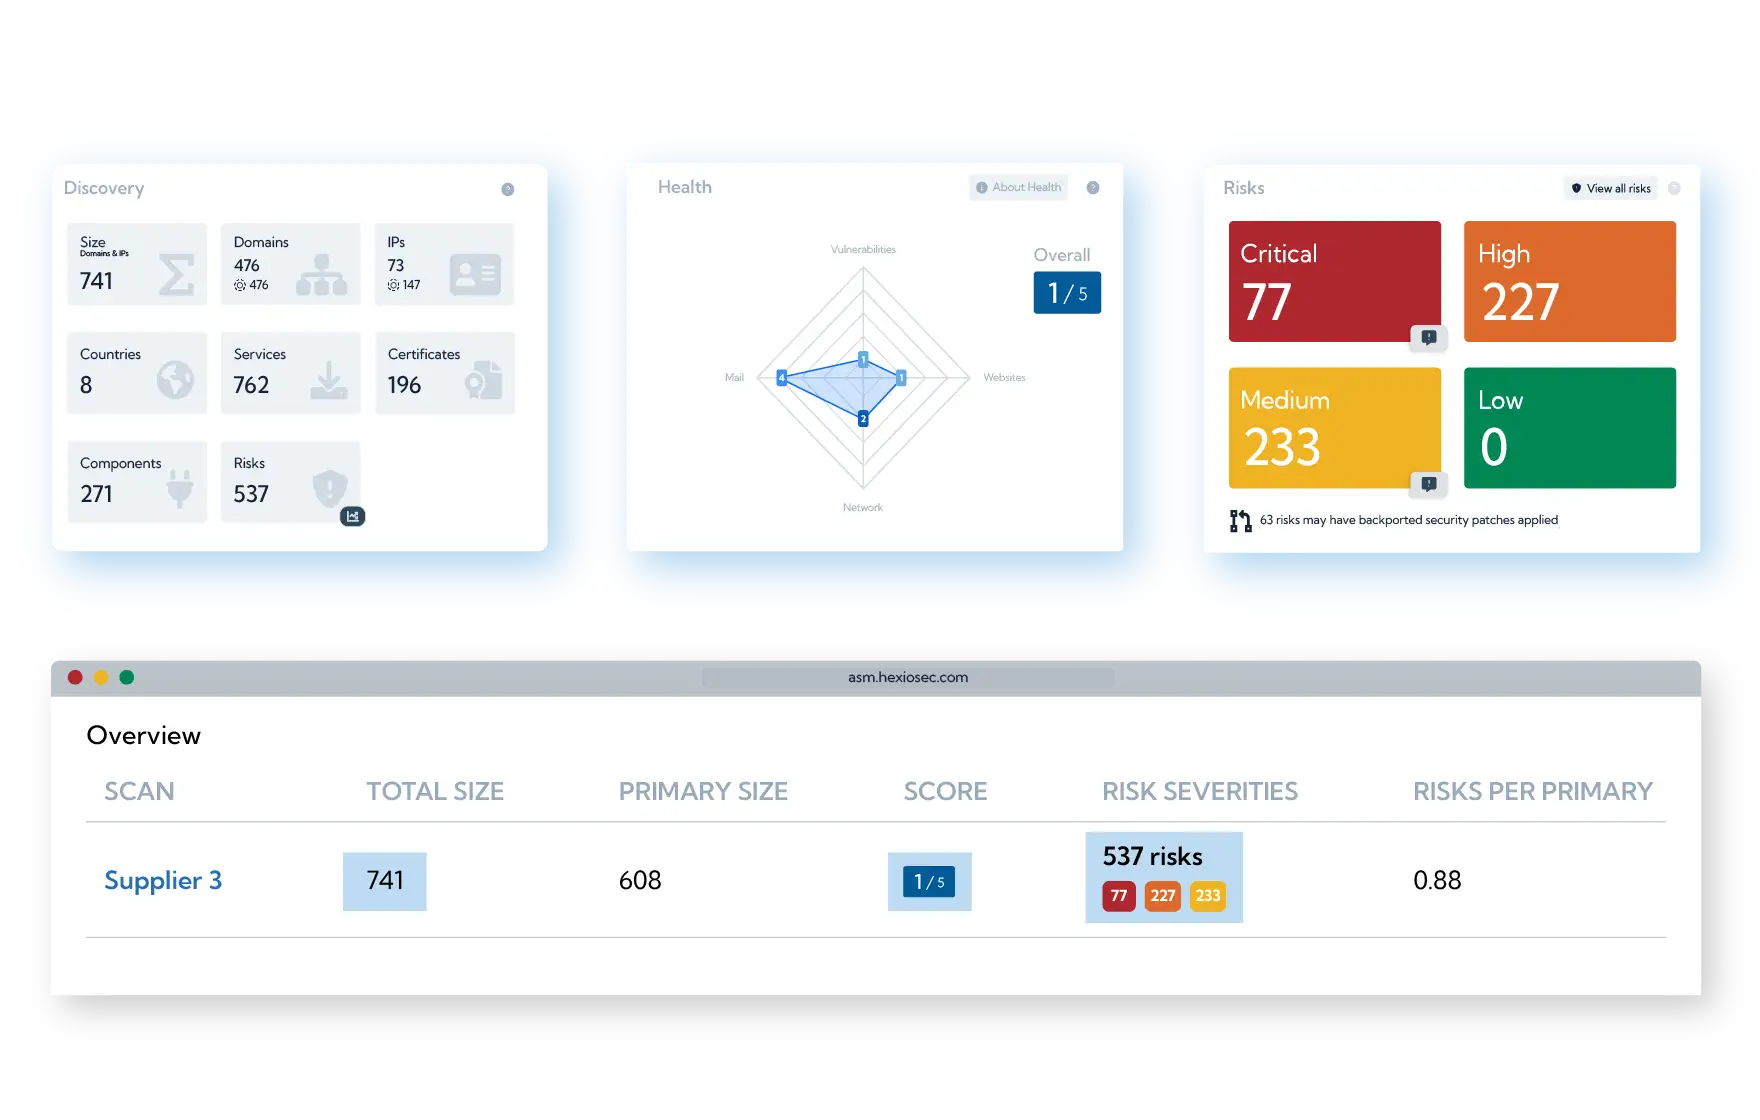
The same discovery you run on yourself
Each supplier gets full external discovery and risk assessment, so you see exposed services and real vulnerabilities rather than a summary grade.
- Full asset discovery per supplier
- Exposed services and known vulnerabilities
- Certificate, mail and DNS hygiene
- Changes flagged as they happen
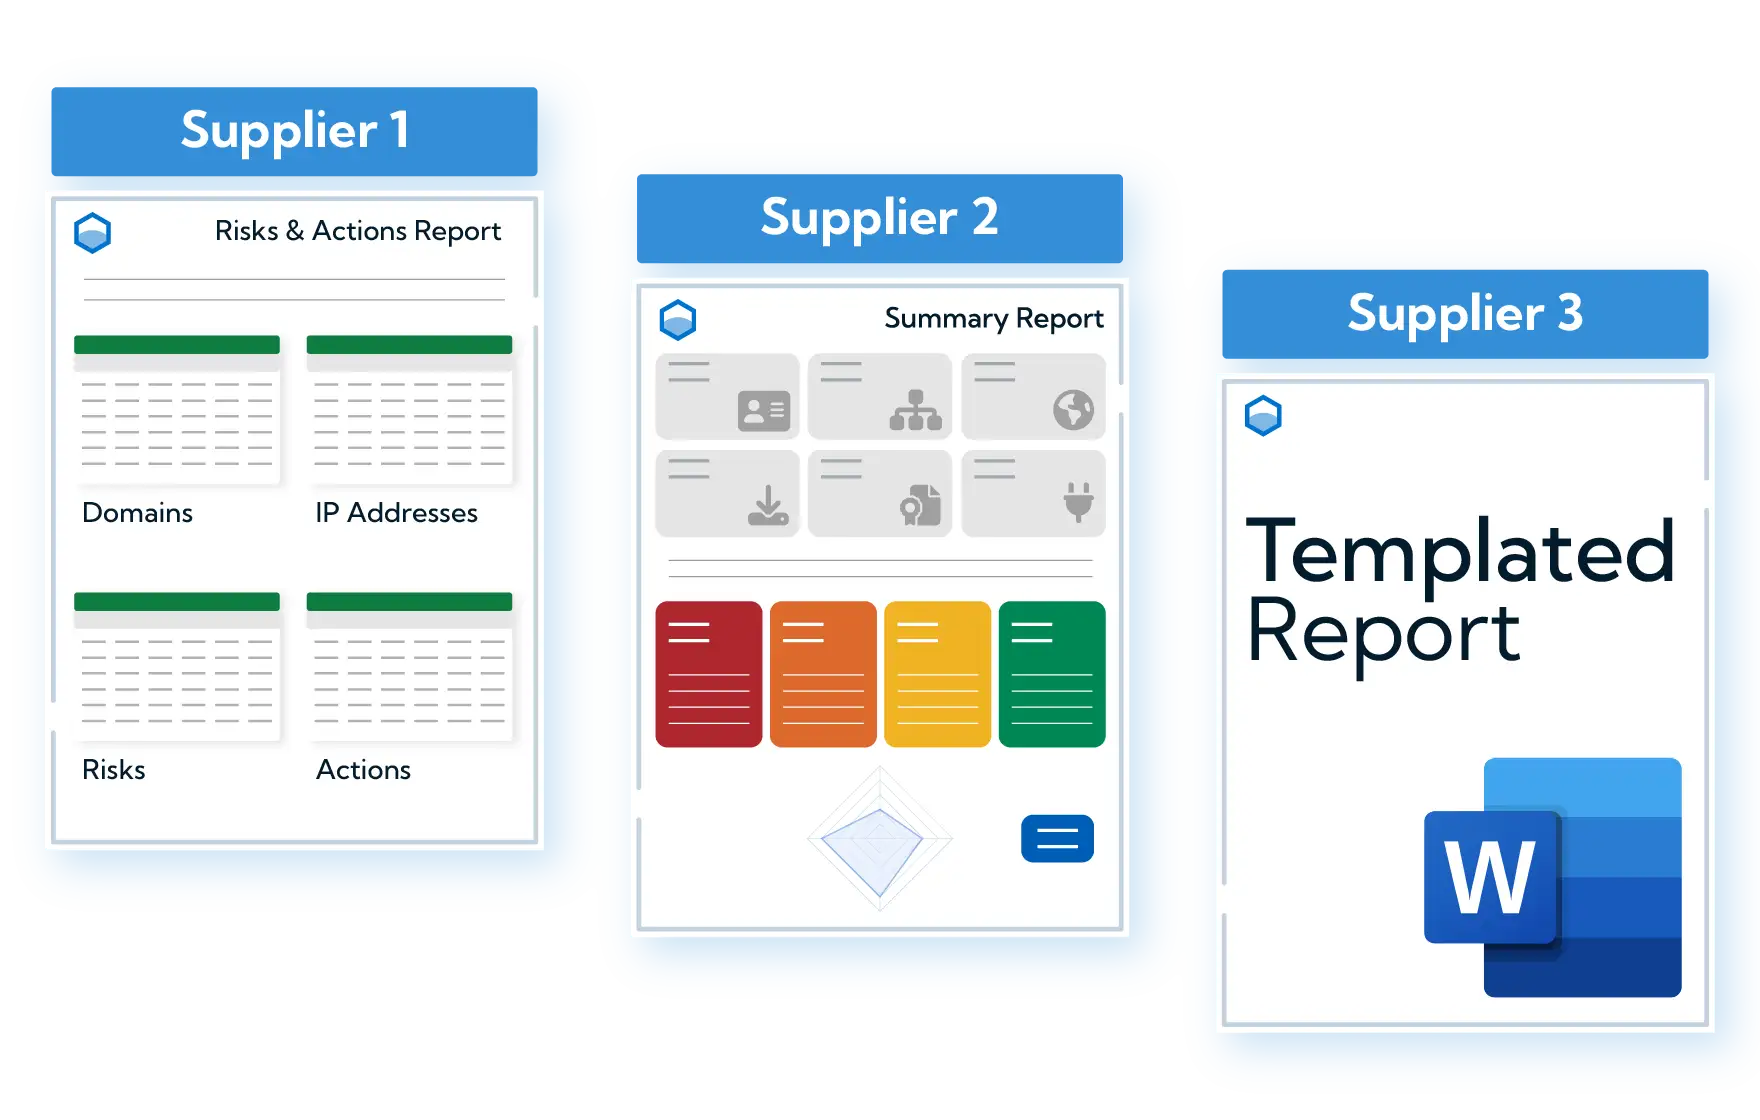
Turn oversight into something you can show
Export supplier posture into the reports your risk committee, auditors and regulators expect to see.
- Per-supplier and portfolio reporting
- Evidence for third-party duties under DORA, CAF and NIS2
- Specifics for remediation and renewal conversations
- A defensible record of ongoing oversight
How supplier monitoring works
Everything here uses the same non-intrusive discovery engine that maps your own estate, pointed at the organisations you nominate.
No supplier involvement needed
Monitoring relies only on publicly available information, so it does not depend on a supplier agreeing to be assessed or returning a form.
The same engine, not a rating
You see the underlying assets and findings, not a score with no working shown.
Comparable metrics
Suppliers are assessed on the same basis, so differences between them mean something.
Change detection
New exposure on a supplier estate is surfaced as it appears rather than at the next review date.
Grouping and criticality
Organise the portfolio by contract, tier or business criticality so attention follows importance.
UK sovereign throughout
Assessment, storage and processing all happen in the United Kingdom, in the London region of Google Cloud.
Where supplier visibility changes the outcome
This page covers the monitoring capability. For the wider programme, including how evidence is collected and acted on, see the supplier risk solution.
ASM + Transfer
Third-party & supply chain risk
Continuous supplier posture, with evidence collected securely through Transfer.
asm led
Achieve compliance
Produce the asset and vulnerability evidence your framework assessment depends on.
ASM + Transfer
M&A due diligence
Assess a target and the suppliers it brings with it, before completion.
ASM Led
Cyber insurance readiness
Show that supplier concentration and exposure are actively managed.
Monitor from outside, collect evidence from inside
External monitoring tells you what a supplier exposes. You will still need documents from them, and that is where Transfer takes over.
- Encrypted forms to request assurance evidence from suppliers
- File collection without exposing a shared mailbox
- A workspace per supplier for ongoing remediation
- UK-sovereign hosting across both products, so evidence never leaves the country
Hexiosec delivers an exceptional experience, principally by enhancing our understanding of customers' digital assets. We've found the platform to be markedly superior to its market counterparts.

Supply chain monitoring on every tier
Start with a single supplier on the free tier. The portfolio dashboard and comparable metrics arrive with Premium.
One supplier
Monitor a single third party alongside your own estate, with the same discovery and risk views.
Three suppliers
Up to three suppliers, with the portfolio dashboard and comparable metrics across them.
Five suppliers & up
From five suppliers, scaled to your portfolio, with portfolio reporting and a named account manager.
Questions about supply chain monitoring
Do we need the supplier to agree?
Is this the same as a security rating service?
How many suppliers can we monitor?
What if a supplier disputes a finding?
Does it cover their suppliers too?
How does this fit our existing assessment process?
See what your suppliers expose
Add your first supplier on a free account, or talk to us about a larger portfolio.