Cyber Insurance Readiness
Go into renewal with evidence, not estimates
Underwriters price uncertainty. If you can't show what you expose to the internet and what you have done about it, you pay for the doubt. Hexiosec gives you the evidence, and a secure way to hand it over.
- UK Sovereign
- Cyber Essentials Plus
- DSIT Software Security Ambassador
- NCSC ACD 2.0 (ASM)
- Trusted by UK Government and regulated industry
The questions got harder and the market got tighter
Cyber cover is no longer a form and a premium. Insurers now assess your external posture themselves, and they will find whatever you didn't declare.
Applications ask what you can't evidence
Questions about unsupported software, exposed services and patching assume an inventory most organisations do not actually maintain.
Underwriters scan you anyway
Many insurers run their own external assessment. Finding something you didn't mention starts the relationship badly.
A claim can turn on a declaration
If what you stated does not match what was exposed, that becomes an argument at the worst possible moment.
The external questions, and whether you can answer them today
These are the things an insurer can check from the outside, which means you should check them first.
Unknown internet-facing assets
Forgotten subdomains, test environments and supplier-hosted sites branded as yours. All visible, all in scope.
Known exploited vulnerabilities
Unpatched issues on the CISA KEV catalogue are the ones underwriters and attackers both care about most.
End-of-life and unsupported software
Publicly visible versions that no longer receive security updates are a common cause of loaded premiums.
Exposed remote access and admin panels
Login pages, management interfaces and remote access services that should not be reachable from the internet.
Certificate and email hygiene
Expired certificates, weak protocols and missing SPF, DKIM or DMARC records that signal loose administration.
Supplier exposure
Increasingly, the estates of the third parties you depend on, especially where they process your data.
What we can evidence, and what we cannot
An insurance application covers more than your external estate. We will not pretend otherwise.
We cover this
What Hexiosec ASM evidences
Your internet-facing estate, the exposure on it, how risks were prioritised, and a dated record of what was remediated.
OUTSIDE OUR VIEW
What we do not see
Backups, endpoint protection, MFA on internal systems, staff training and incident response readiness all sit outside external discovery.
WE CAN STILL HELP
Where our consultants help
If the application exposes gaps in governance, architecture or process, our team works with you on the parts a scan cannot fix.
Three parts of the same problem
Find it, fix it, and hand the evidence over without emailing a map of your weaknesses.
The evidence

Hexiosec ASM
Continuously discovers your external estate, ranks exposure by real-world exploitability, and produces dated evidence of remediation.
THE HANDOVER

Hexiosec Transfer
Sends that evidence to your broker or underwriter with encryption and an audit trail, rather than as an email attachment.
THE REMEDIATION

Hexiosec Consulting
Helps you close the gaps that are affecting price or blocking cover, and meet the conditions attached to a policy.
See what the underwriter will see, first
Run the same kind of outside-in assessment an insurer would, months before the form lands. Most organisations find something in the first scan that would have been awkward to explain and simple to fix.
- A complete view of your internet-facing estate
- Exposure ranked by what is actually exploited
- The chance to fix the obvious before it is on record
- A defensible answer to every external question
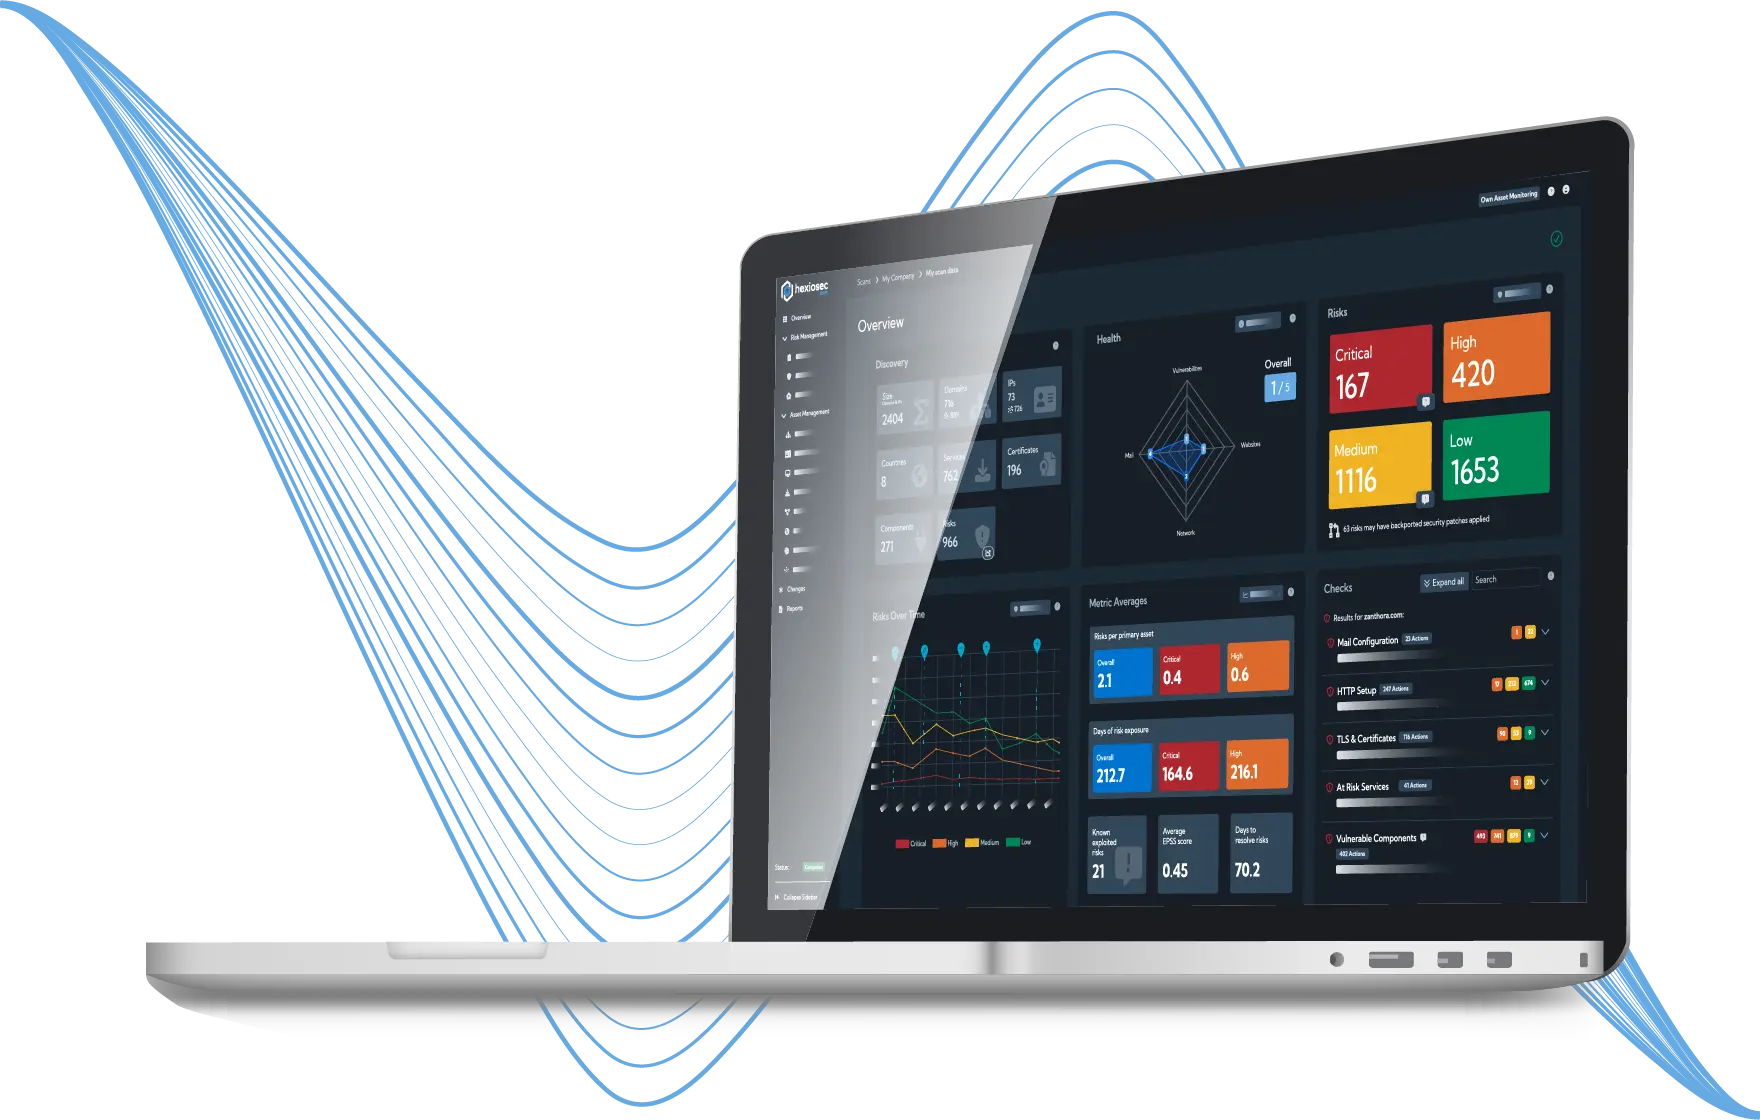
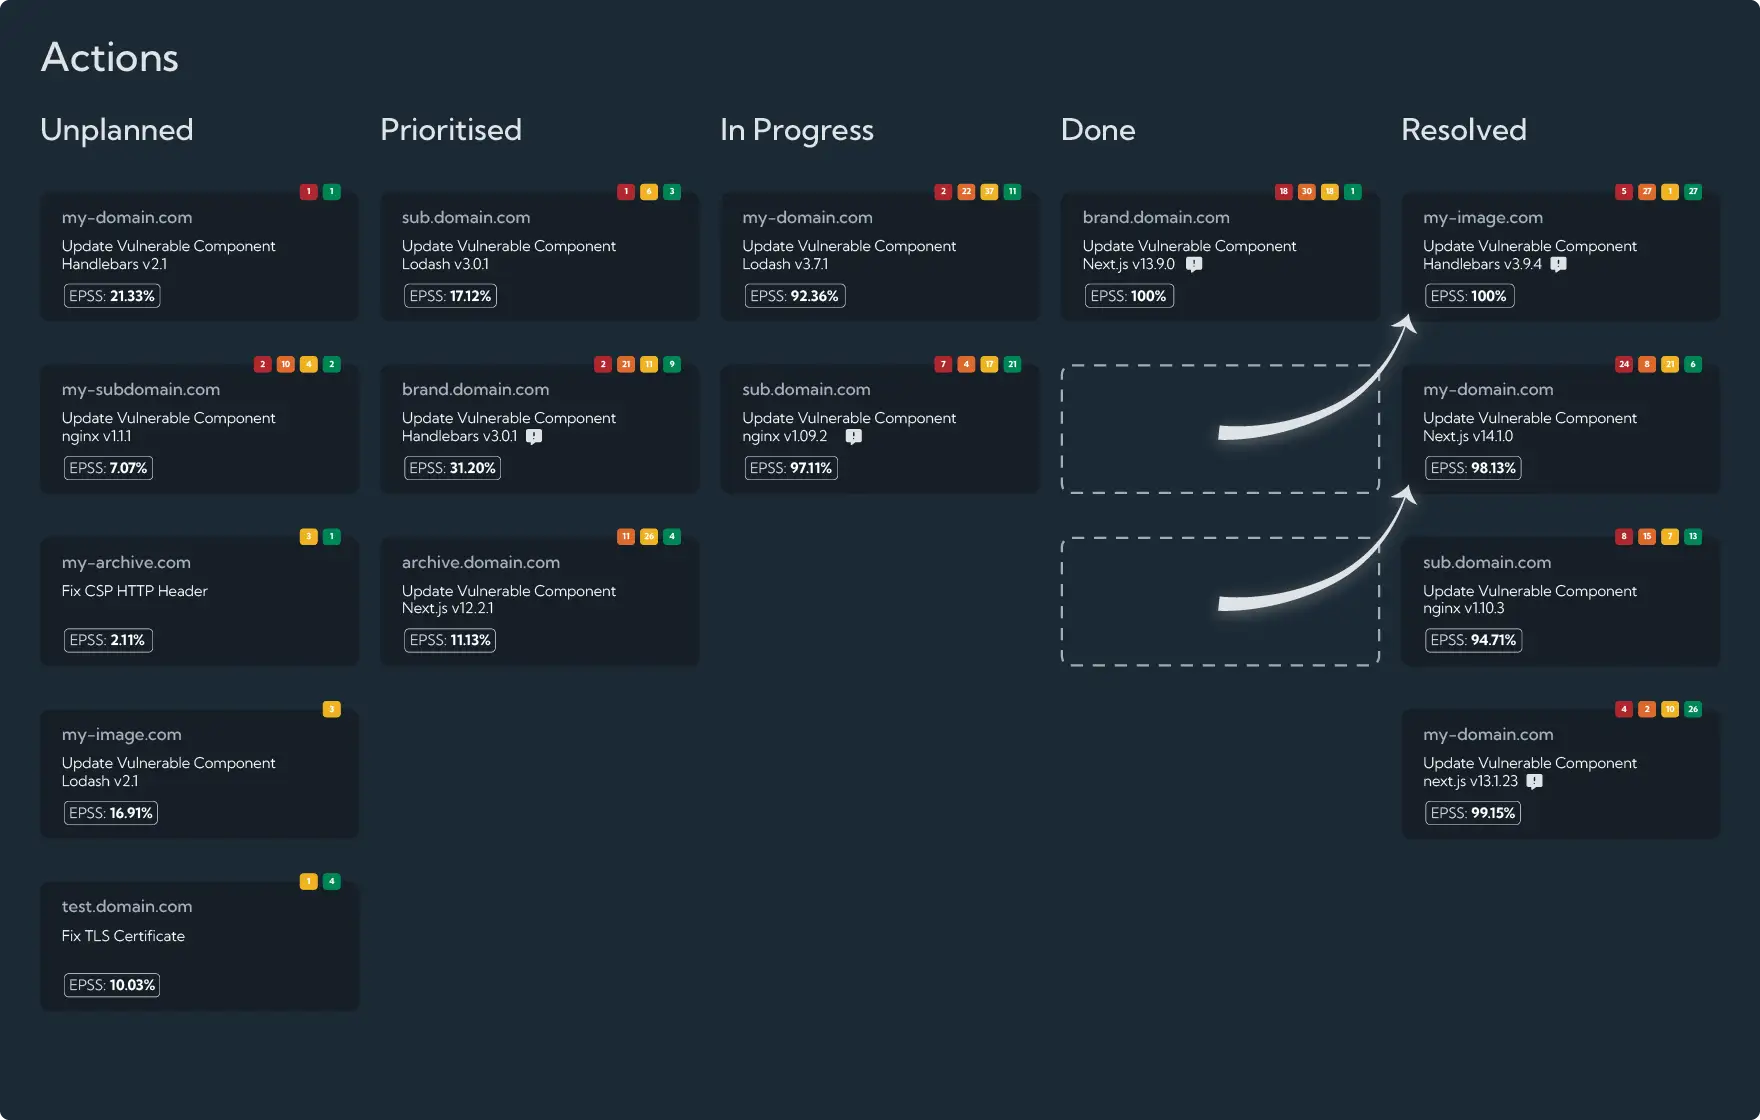
Answer with dates, not adjectives
Saying you take patching seriously means very little. Showing when an issue was found, when it was closed and what the estate looks like now is a different conversation, and it is one underwriters respond to.
- Dated discovery, remediation and closure records
- Trend showing exposure reducing over time
- Exportable evidence packs for brokers and underwriters
- Secure delivery through Hexiosec Transfer
What renewal looks like in your world
Legal
Client data concentration and merger-inherited estates make law firms a scrutinised class of risk.
Wealth and asset management
Regulated firms face both DORA duties and insurer questions on the same underlying evidence.
Healthcare
Large clinical estates and sensitive data mean external exposure is examined closely.
Government
ALBs and local government carry the same questions through different assurance routes.
By focusing on high-impact, externally visible risks, the university improved cyber resilience, reduced exposure, and secured a 10% reduction in cyber insurance premiums.
Start before the form arrives
The earlier you look, the more of it you can fix rather than declare.
Scan my domain
See your external estate in minutes, with no account. This is the same view an underwriter can build.
Monitor continuously
A free account keeps 50 assets under weekly monitoring. Premium adds daily monitoring and exportable reports.
Talk it through
If renewal is close or cover is conditional, speak to an engineer about the fastest route to evidence.
Questions about insurance and evidence
Will this reduce our insurance premium?
Do insurers accept this as evidence?
Can you complete the insurance application for us?
We already had a penetration test. Is that enough?
How long before renewal should we start?
Does this cover our suppliers?
See what your insurer will see
Run a free scan of your domain before the next application lands.