Hexiosec ASM
Continuous external attack surface management
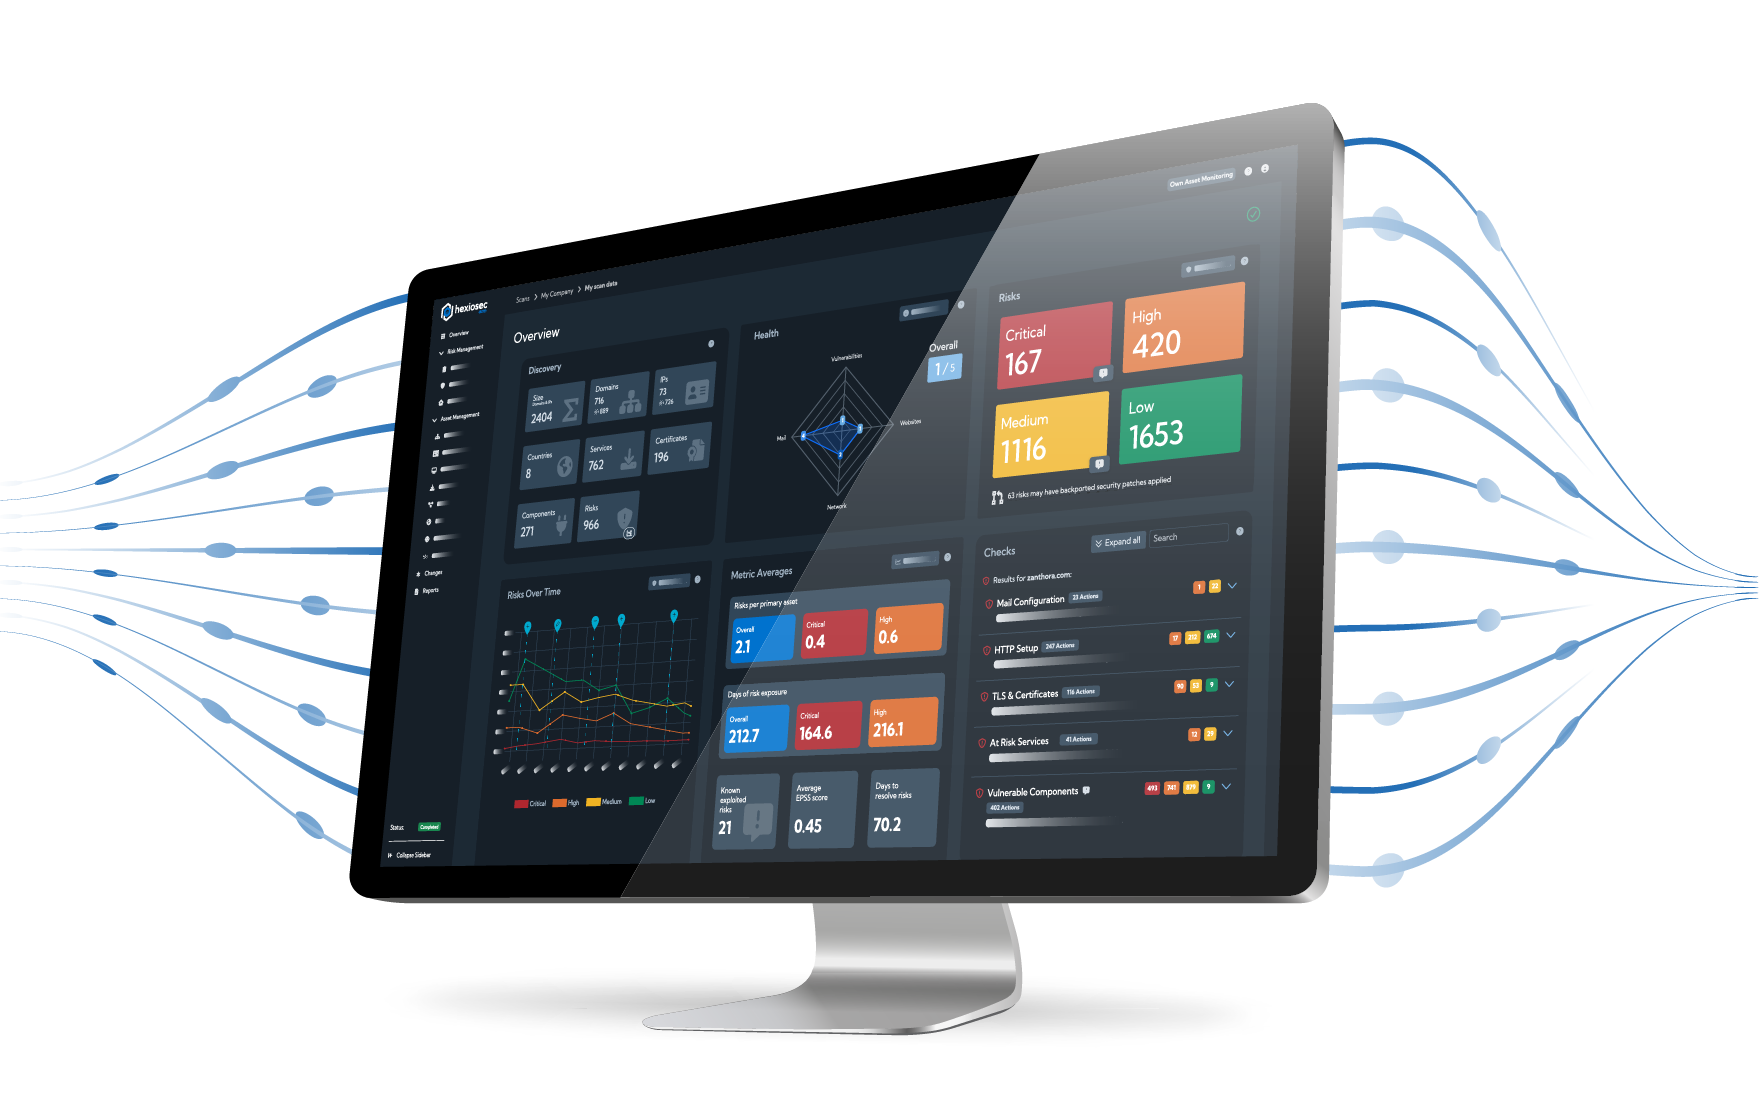
See your digital estate the way attackers do. Hexiosec ASM starts from one domain, maps everything connected to it, ranks what is most likely to be exploited, and tells you when something changes. Built by engineers who used to do this work inside UK government.
- No account needed
- Non-intrusive discovery
- Most scans in minutes
Trusted by teams who cannot afford an unknown asset




Your attack surface is bigger than your asset list
Cloud projects, forgotten subdomains, supplier portals and shadow IT all reach the internet without asking anyone first.
Most estates are far larger than the spreadsheet that describes them.
You can't inventory what you can't see
Digital estates change weekly. Asset inventories quickly become outdated and instantly go stale the moment a team spins something up.
Scanners need a target
Traditional tools test what you point them at. They rarely discover forgotten assets, shadow IT, or internet-facing systems no one remembers.
Auditors ask for evidence
Frameworks increasingly expect proof of asset management and vulnerability visibility. Evidence must be accurate, current, and available on demand.
Four conversations that go better with evidence
Attack surface management tools are a means to an end. They provide the evidence behind the conversations that drive critical business outcomes.
WIN AND KEEP CLIENTS
Answer security questionnaires with evidence
When a client or a procurement panel asks how you manage your estate, show a live inventory and the exposure attached to it.
PASS ASSESSMENTS
Evidence asset and vulnerability management
CAF, NIS2, DORA and DSPT all expect it. Produce it on demand instead of rebuilding it before every assessment.
REDUCE PREMIUMS
Go into renewal with numbers, not estimates
Underwriters price uncertainty. An accurate asset count and a clean exposure picture change that conversation.
MANAGE SUPPLIERS
Oversee the suppliers who hold your data
Continuous third-party posture, rather than an annual questionnaire nobody verifies.
Start with one domain. See the whole estate.
Hexiosec ASM maps everything connected to your seed domain, then keeps watching it. Assets, services, certificates, the associated risks and the guidance to remediate them, on a schedule rather than as a project.
Five capabilities. One continuous view.
Every capability runs on the same non-intrusive discovery engine. Pick where you need to go.
Asset discovery
Find every internet-facing asset from one seed: subdomains, IPs, services and certificates.
Risk management
Prioritise with CVEs, KEVs and EPSS, grouped by root cause so one fix can close several findings.
Supply chain monitoring
Watch the external exposure of your suppliers, with comparable metrics across the portfolio.
Actionable insights
Reports and exports that turn findings into prioritised decisions, evidence and board updates.
Cloud connector
Inside out discovery across AWS, Azure and GCP. Read-only, least privilege, controlled by you.
From a domain to a plan, in four steps
Seed
Input your domain, an IP range or an email domain. Nothing to install.
Discover
We map the connected estate non-intrusively, using only publicly available information.
Prioritise
Risks are ranked with KEV and EPSS, so you fix what is genuinely exploitable first.
Act and monitor
Work the actions, then let continuous monitoring surface every change.
A UK sovereign alternative to the big platforms
British built, British hosted
Designed and operated in Cheltenham by former UK government, defence and intelligence engineers. Your data stays in the UK by default.
Chosen for the NCSC ACD 2.0 trials
One of the suppliers selected for the trials that validated external attack surface management as a security control.
Exploitability, not noise
KEV and EPSS rank what attackers are actually exploiting, so your team works the risks that matter.
Transparent and self-service
A free scan with no account, published pricing, and real engineers to talk to when you need them.
Built for the outcomes you are judged on
Hexiosec ASM works alongside Hexiosec Transfer and Hexiosec Consulting Services wherever exposure meets sensitive data.
asm led
Achieve compliance
Evidence asset and vulnerability management for CAF, NIS2, DORA and DSPT.
ASM Led
Cyber insurance readiness
Accurate exposure data and a controlled remediation process makes an easier conversation at renewal.
ASM + Transfer
Third-party & supply chain risk
Continuous supplier posture, with the evidence collected securely.
ASM + Transfer
M&A due diligence
See what you are buying, then run the deal in a secure data room.
Built for regulated work
See how Hexiosec supports your sector, across external exposure and secure information exchange.
Wealth and asset management
DORA third party duties, FCA expectations and estates built up through consolidation.
The platform finds it. Our engineers help you fix it.
Software surfaces the problem. Sometimes what you need next is a person: a remediation plan you can resource, or an architecture review before you rebuild.
- Remediation planning and prioritisation with your team
- Infrastructure and cloud architecture review
- Migration and hardening support for legacy services
- Governance, policy and process development
Hexiosec ASM is so easy to get going with, and a massive win for identifying vulnerabilities, and have them analysed in terms of risk so you can focus attention in the right area at the right time.
Evidence, not adjectives
Independently assessed, UK sovereign, and one of the suppliers chosen for the NCSC ACD 2.0 trials that established what this control should look like.
- NCSC ACD 2.0
- Cyber Essentials Plus
- UK sovereign hosting
- DSIT Software Security Ambassador
- Government Commercial Agency
Start free. Upgrade when the estate demands it.
Published pricing, a free tier that does not expire, and a scan you can run before any of it.
£0
No card required, free forever
Up to 50 assets. Weekly monitoring. Core views, actions and a summary report. Up to 5 users.
From £299
Per month, billed annually
Up to 300 assets. Daily monitoring. Full risk workflow, downloadable reports and tagging. Up to 10 users.
On request
Scoped to your estate
Larger estates. API access, ad hoc scanning and a named account manager.
Questions, answered honestly.
What is external attack surface management?
How is this different from a penetration test?
Do you need permission to scan?
Where is our data held?
Can we start without talking to sales?
How long until we see results?
See your assets the way an attacker does
Enter your domain for an instant snapshot of the assets your organisation has facing the internet. The same public footprint an attacker maps first. No sign-up, results in seconds.